MOVEit Hunting Cl0p
Threat Hunting with Cyborg Security & CISA Alert for #StopRansomware: CL0P Ransomware Gang Exploits CVE-2023–34362 MOVEit Vulnerability
MOVEit Hunting Cl0p
Threat Hunting with Cyborg Security & CISA Alert for #StopRansomware: CL0P Ransomware Gang Exploits CVE-2023–34362 MOVEit Vulnerability
The RaaS group Cl0p has repeatedly made headlines in recent weeks with various new methods to access victim systems via vulnerabilities with the main motivation of doing double extortion and encryption.
While vulnerabilities such as PaperCut and GoAnywhere were successful campaigns by the attacker in the spring of this year, Cl0p is making headlines in June 2023 with a new MOVEit vulnerability that they published on 5th of June to steal data with the exploit.
How can you analyze this vulnerability as quickly as possible and hunt for indicators as well as test possible attacks by yourself?
In this article I would like to present a fast and cost-effective analysis with various OSINT tools, which I use as an analyst from a thread informed approach.
Let’s start with the CISA report, whose MITRE ATT&CK techniques can be extracted either via the D3FEND Attack Extractor or via Scott Small’s Python tool webpage2attack which is creating from the website directly a JSON file. See also this article.
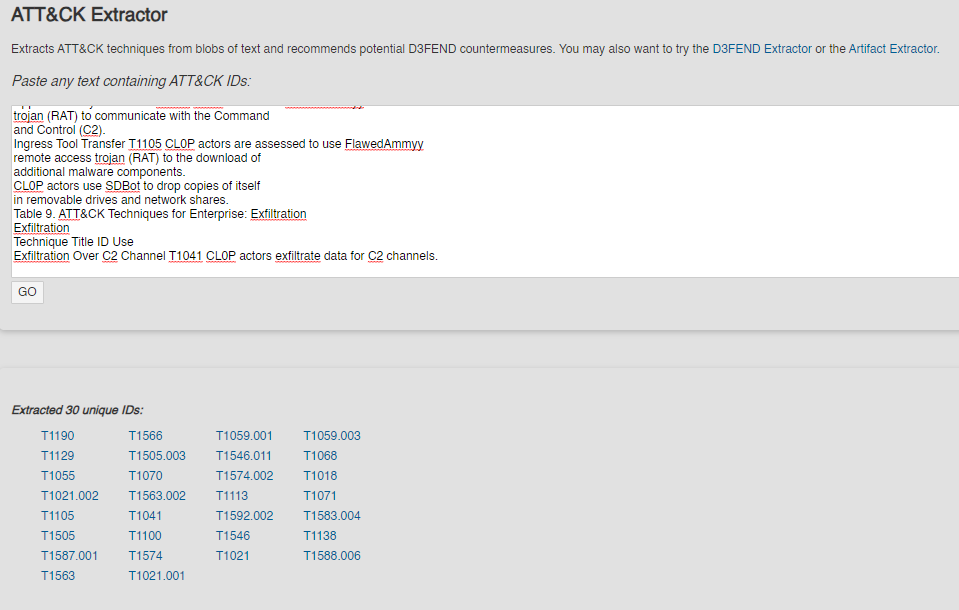
Fast extraction of MITRE ATT&CK techniques for countermeasures

Fast extraction from the website with the webpage2attack Pyhton script
The latest alert on MOVEit, which was just released today, can now be uploaded to Tidal Community Edition and be compared with other CTI reports of the latest TTPs and software for Cl0p. In the Enterprise Edition you can submit for e.g new software and procedure examples. To get more information about how to work with the platform and a guidance about cyber threat profiling, please visit the website.

Cyber Threat Profiling for Cl0p with the Tidal Cyber Community Edition
Next, you can design with Att&CK Flow a playbook for MOVEit. Here, the MITRE ATT&CK techniques can be designed according to the order of the TTPs and exploits used. This can be especially useful if there are different playbooks for the same attacker and you need an overview of the respective MITRE ATT&CK techniques, software, procedure example and artifacts. In the case of encryption, the Att&CK flow helps to understand how the attacker got into the systems and facilitates the search for artifacts and procedure examples.

Att&ck Flow for Cl0p MOVEit

PaperCut Att&ck Flow for Cl0p and LockBit
If you now know the attacker’s approach, you would like to understand in the sense of a Threat Informed Defense on the one hand whether the attacker may have already used this vulnerability and whether you would recognize the attack and if the security tools in your environment would trigger an alert.
For this you can now use from Cyborg Security The HUNTER platform, which is available in a community edition— similar to the CTI platform Tidal.
With The HUNTER Platform, you have access to a constantly updated library of expertly-crafted hunt content and a set of tools for managing and executing hunts, all in one place, that allows you to streamline the hunt process and improve the efficiency of your team while they protect your organization from cyber threats. HUNTER is a powerful threat hunting platform designed to help organizations proactively detect and respond to cyber threats.
Since MOVEit is very up to date and the analysts of Cyborg Security pretty fast, you will find vulnerability information and several hunting packages at the top of the first page also in the community version for the new exploit. Some of them have to be paid, others are freely available to the community.

Free Hunt for recently updated hunt packages
I immediately took the first free available hunt for MOVEit created today. You can get the hunt packages for several known EDRs, XDR and Endpoint detections like CrowdStrike, Microsoft Defender, Microsoft Sentinel, Palo Alto Cortex XDR, QRadar Query and Splunk and start to hunt by directly deploying the hunts to your system with the “Add tool URL to open in Microsoft Defender” button for MDE as an example.

You can copy the hunts or you can directly deploy the hunt into your system
You get additionally an analyst note and the query logic to verify the hunt.

Research and query logic explained for the hunt package
In addition to the possibility to hunt on various systems, you can also use a Cyborg Security own developed Atomic Red Team test to test the exploit rapidly in your environment. This is ALSO for free! You just have to download the test and copy it into your own existing atomics folder.

Invoke-AtomicTest T1505.003 developed test by Cyborg Security
In this test, the corresponding malicious files are copied to a specific folder. This test simulates an adversary leveraging Web Shells by simulating the file modification to disk. Idea from APTSimulator. cmd.aspx source — https://github.com/tennc/webshell/blob/master/fuzzdb-webshell/asp/cmd.aspx
As always, you can use Sysmon to verify the test and which IDs would be triggered.

Windows Command Shell execution of xcopy.exe

Malicious File Event 11
With the help of the HUNTER platform, you can now not only create a playbook within a few hours, but also proactively hunt for attackers in several systems for free and create a threat profile to understand the latest attacks for the related threat actors.
I really don’t know why Cyborg Security is not more recognized in the field. This platform is really unique and a great opportunity to manually verify the own security posture within a few hours after a recent exploit or vulnerability is released.
Please check out their website for more information.
메타데이터
- post_id
- 101c93e3fef1
- slug
- moveit-hunting-cl0p-101c93e3fef1
- url
- https://medium.com/@simone.kraus/moveit-hunting-cl0p-101c93e3fef1
- canonical_url
- https://medium.com/@simone.kraus/moveit-hunting-cl0p-101c93e3fef1
- author_url
- https://medium.com/@simone.kraus
- status
- ok
- fetched_at
- 2026-08-20 21:57:23