br0ken — crackme1
Introduction
br0ken — crackme1
Introduction
Language: C/C++
Platform: Windows
Arch: x32
Crackmes.one: https://crackmes.one/crackme/5ab77f5333c5d40ad448c100
Debugging/Reversing
Alright so finally I found a really nice crackMe which is very enjoyable to me to debug!

It does couple stages which actually makes it funnier than other crackMes because it has levels which you go one by one to finish it up!

So we will go stage by stage.
Stage-1:
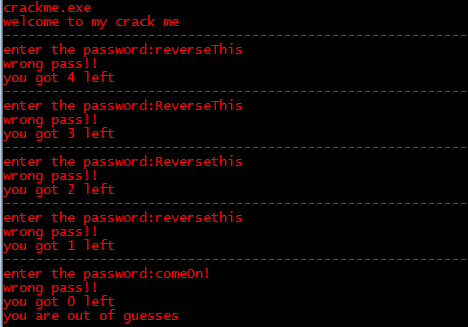
Alright so our first target is to find password to pass second stages. So for that purpose I would like to start from strings to check and see is there any string which let us to find first stage codes.

Yes! look, there is console messages and also some interesting strings to note for example first one “QbTTx1sE”, we will keep eye on it!
Now let’s double click the “Enter Password To Continue” String to find out where our input is being kept so knowing how it is being called to compare real password.

Pretty straightforward, just one thing to notice that password should have 8 characters otherwise it jumps fail message right away!
So we can only type 8 digit so let’s put “12345678”

So we can see that this whole block is increasing our input by “1” so the input “12345678” to “23456789” and it is being compared with the string we found earlier so in that case, can we say that if we decrease that string’s characters by “1”, we can get the correct password. Let’s do that.

Here we can see that red squares are representing the encrypted string and green ones are our password so the password is “PaSSw0rD” funny!

Stage-2:

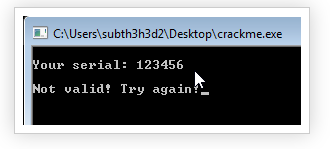
After reading serial, we get this block of code which is basically going through name input and doing some calculation and at the end is comparing the result of name input calculation and inputted serial.

Here is the python version of the algorithm so let’s type “reverseThis” in name and 1160 to serial.

Boom! we got it too!
Stage-3:

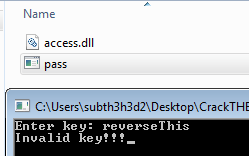
In this stages, we just need patch it to remove unwanted message from above block

Done!
We will not bypass any check, let’s leave this one as it is :)
Conclusion
Thanks to writer, I really really enjoyed!
REv3rs3Th3P14n3t
메타데이터
- post_id
- 27546d8e40a
- slug
- br0ken-crackme1-27546d8e40a
- url
- https://medium.com/@4d5ah/br0ken-crackme1-27546d8e40a
- canonical_url
- https://medium.com/@4d5ah/br0ken-crackme1-27546d8e40a
- author_url
- https://medium.com/@4d5ah
- status
- ok
- fetched_at
- 2026-07-27 00:46:47