Scaling Startups with Enterprise Risk Management Software for 2026
Enterprise risk management software has become the baseline requirement for high-growth startups aiming to secure institutional capital and…
Scaling Startups with Enterprise Risk Management Software for 2026
Enterprise risk management software has become the baseline requirement for high-growth startups aiming to secure institutional capital and satisfy regulatory bodies in 2026.
Rather than treating compliance as a hurdle to be cleared before an IPO, emerging companies use these platforms to build scalable governance into their technical architecture, replacing manual audits with automated, real-time monitoring. This approach relies on predictive intelligence to identify financial anomalies and operational risks before they impact the bottom line, ensuring that internal controls function as an active defense rather than a static policy.
By establishing a data-driven foundation early in the lifecycle, startups provide investors with verifiable proof of operational integrity, turning risk mitigation into a strategic asset for rapid expansion.

Enterprise Risk Management Software
The Friction of High-Velocity Growth
I spent a weekend last month reviewing the books of a fintech startup that had grown from fifty employees to five hundred in less than a year. On the surface, the numbers were staggering, but underneath, the plumbing was leaking. They were using a messy collection of spreadsheets and Slack channels to manage their vendor approvals and payment authorizations. It was a disaster waiting for a Department of Justice subpoena. This is the “growth trap” most founders fall into: they focus so much on the product that they ignore the infrastructure required to protect it.
The reality is that your risk profile doesn’t grow linearly; it grows exponentially. As you add more vendors, more regional offices, and more employees, the number of possible points of failure explodes. If you wait until you are a multi-billion dollar entity to implement enterprise risk management software, you are essentially trying to install a flight computer while the jet is already at thirty thousand feet. It is expensive, dangerous, and often too late.
Engineering Scalable Governance into the Core
We have to stop thinking of risk management as an administrative burden. In 2026, it is a data science problem. You don’t need an army of auditors checking receipts; you need a system that functions like a biological nervous system. This means your financial systems should have “reflexes” that stop suspicious activity the moment it occurs.
- Sub-second Transaction Analysis: Moving beyond batch processing to monitor every payment and ledger entry as it happens.
- Behavioral Linkage: Normalizing data from disparate tools like Slack, Jira, and your ERP to find hidden conflicts of interest or internal collusion.
- Immutable Audit Logs: Generating machine-readable trails for every decision to meet the “show your work” requirements of modern regulators.
- Automated Vendor Onboarding: Integrating sanctions screening and identity resolution into the initial contract phase rather than as a post-mortem check.
I recently watched a reasoning agent flag a series of split-payments in a startup’s procurement department. Individually, the payments were small enough to bypass human approval. Combined, they represented a six-figure kickback scheme that had been running for six months. A human auditor looking at a sample would have missed it. The software caught the pattern in seconds because it wasn’t looking at the transactions; it was looking at the intent behind the data.
The Real ROI of Risk Tech
Most leadership teams view compliance as a cost center, but the ROI of risk tech is actually found in your ability to move faster. When you have a unified view of your organization’s risk, you can take bold moves with confidence. You know exactly where your boundaries are. This visibility is what allows you to enter high-risk markets or launch complex financial products without having to hire a hundred new compliance officers.
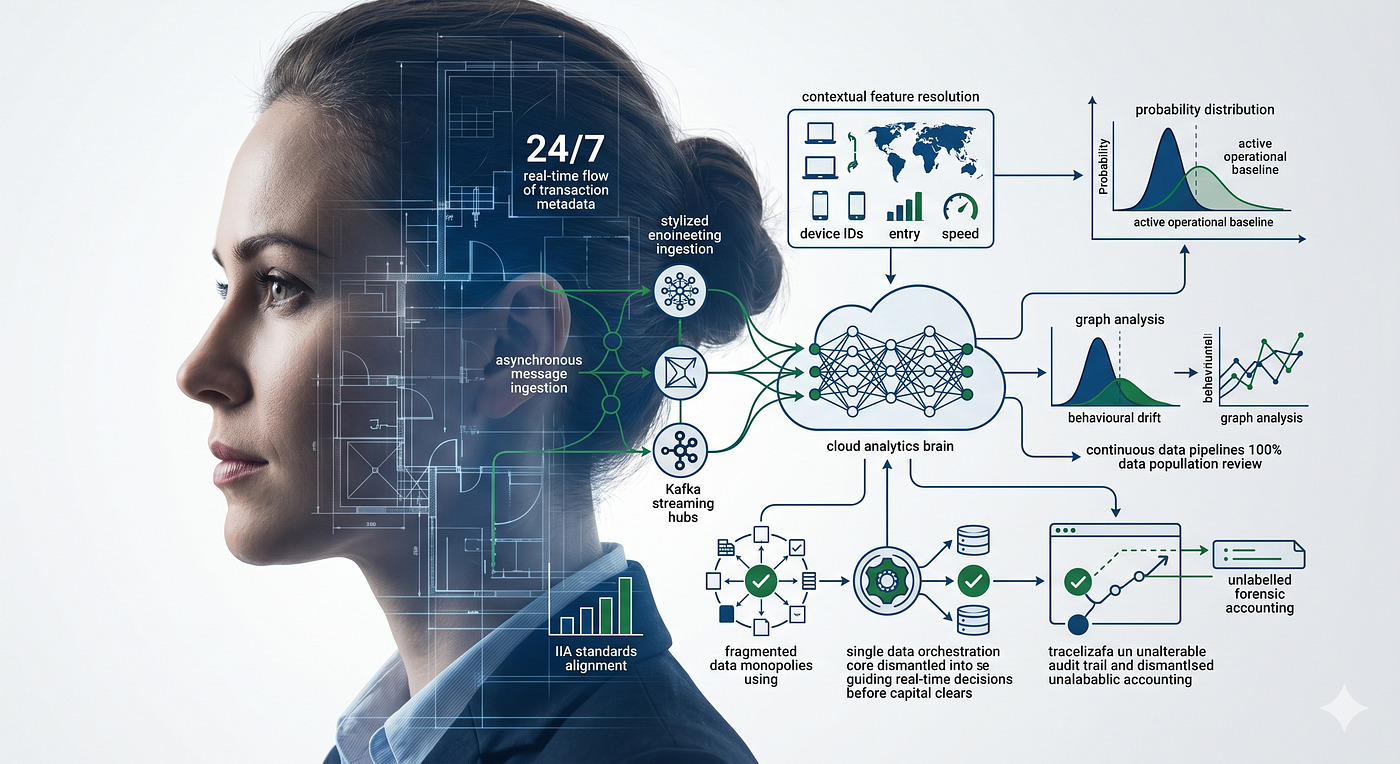
Breaking silos is a leadership task. Startups are notorious for having “shadow zones” where departments use their own tools and processes without oversight. You have to be willing to invest in the data pipelines that feed into a centralized intelligence layer. Organizations that successfully implement these platforms usually adopt a “hub and spoke” model, where individual teams keep their preferred tools but report to a cloud-resident brain. This shift toward continuous monitoring is the single most effective way to reduce regulatory friction and improve operational resilience.
Predictive Intelligence over Reactive Cleanup
I am tired of seeing companies brag about their “remediation” efforts after a scandal breaks. Remediation is just a fancy word for cleaning up a mess that should never have happened. Predictive intelligence allows you to move the conversation from “what went wrong” to “what is about to go wrong.”
This requires a move toward enterprise risk management software that uses machine learning to establish a baseline of “normal” business activity. Once that baseline is set, the system can flag even subtle deviations. If a vendor suddenly changes their bank details to an offshore account that shares a digital fingerprint with a high-risk entity, the system should block the payment before a human even sees it.
The Evolution of Internal Controls
The role of the auditor is changing from a “gatherer” to an “adjudicator.” I don’t want my best analysts spending their days matching decimal points on invoices. I want them looking at the “weird” cases that the system flags. This requires a move toward a more tech-savvy workforce that understands how to audit an algorithm, not just a spreadsheet.
Internal controls shouldn’t live in a PDF manual that sits on a shelf. They should live in the code of the company. Policies should be baked into the deployment scripts of your financial systems. This ensures that compliance is a silent, automated, and unshakable standard that supports every strategic move you make. It turns the “trust but verify” model into a “verify and then trust” model, which is the only way to scale a digital-first institution in the 2026 landscape.
Solving the Regulatory Wall
Regulators are no longer impressed by a list of well-worded policies. They want to see functionality. They want to know that your internal controls actually work in the wild. If you cannot explain why a transaction was blocked or why a specific risk was flagged, you are going to have a very expensive conversation with federal authorities.
Engineering trust with authorities is built on transparency. This is why we focus on “white-box” intelligence. Every choice made by the system must generate a log that a human can follow. As your startup grows, this becomes your primary defense. When a regulator asks why you didn’t catch a specific bribe, “we didn’t look at that sample” is a losing answer. Proving that you had a system in place that could have caught it; and that you took action on the signals you did receive, is the definition of corporate defensibility.
The Cost of Procrastination
Waiting for the “perfect” time to modernize is a form of procrastination that carries a massive price tag. While you wait, your competitors are training their models and gathering the data needed to make their systems smarter. In the world of machine learning, the person with the most data almost always wins.
If you start your automation journey now, you might have a defensible core by next year. If you wait until you are under investigation, you have already lost.
Moving to autonomous operations is the only way to stay relevant. It turns compliance from a cost center that “finds mistakes” into a source of strategic insight that allows you to scale with absolute confidence.
Also Read: The ROI of Autonomous Compliance Workflows and Agentic AI
메타데이터
- post_id
- 2967a4c94c83
- slug
- scaling-startups-with-enterprise-risk-management-software-for-2026-2967a4c94c83
- url
- https://medium.com/@manish.pandey27/scaling-startups-with-enterprise-risk-management-software-for-2026-2967a4c94c83
- canonical_url
- https://medium.com/@manish.pandey27/scaling-startups-with-enterprise-risk-management-software-for-2026-2967a4c94c83
- author_url
- https://medium.com/@manish.pandey27
- status
- ok
- fetched_at
- 2026-06-09 15:37:30