Passive Recon through ExifTool, Social Engineering and WiGLE
ExifTool is an application for reading and modifying multimedia files such as images. Information contained in an image can be a starting…
Passive Recon through ExifTool, Social Engineering and WiGLE
ExifTool is an application for reading and modifying multimedia files such as images. Information contained in an image can be a starting point for performing social engineering. This article presents the methodology to retrieve information stored in an image from a TryHackMe Room using ExifTool. The information gathered from the image’s metadata will be used for social engineering to obtain additional information about the author. Important information will be analyzed in a key-value format using an online wireless hotspot database — WiGLE.
Part 1: Retrieve the metadata of an image file
Part 2: Retrieve the author’s information through Social Engineering
Part 3: Use WiGLE API to find out the SSID information from a BSSID
TryHackMe Room — OhSINT
Part 1: Retrieve the metadata of an image file
To begin with, ExifTool provides an easy method to retrieve the metadata of an image file. Running ExifTool on a Linux OS, the command to extract information from an image is as follows.
exiftool WindowsXP.jpg
After executing the command, information such as Copyright appears. The most interesting information on the image is copyright information, which is stated as OWoodflint.
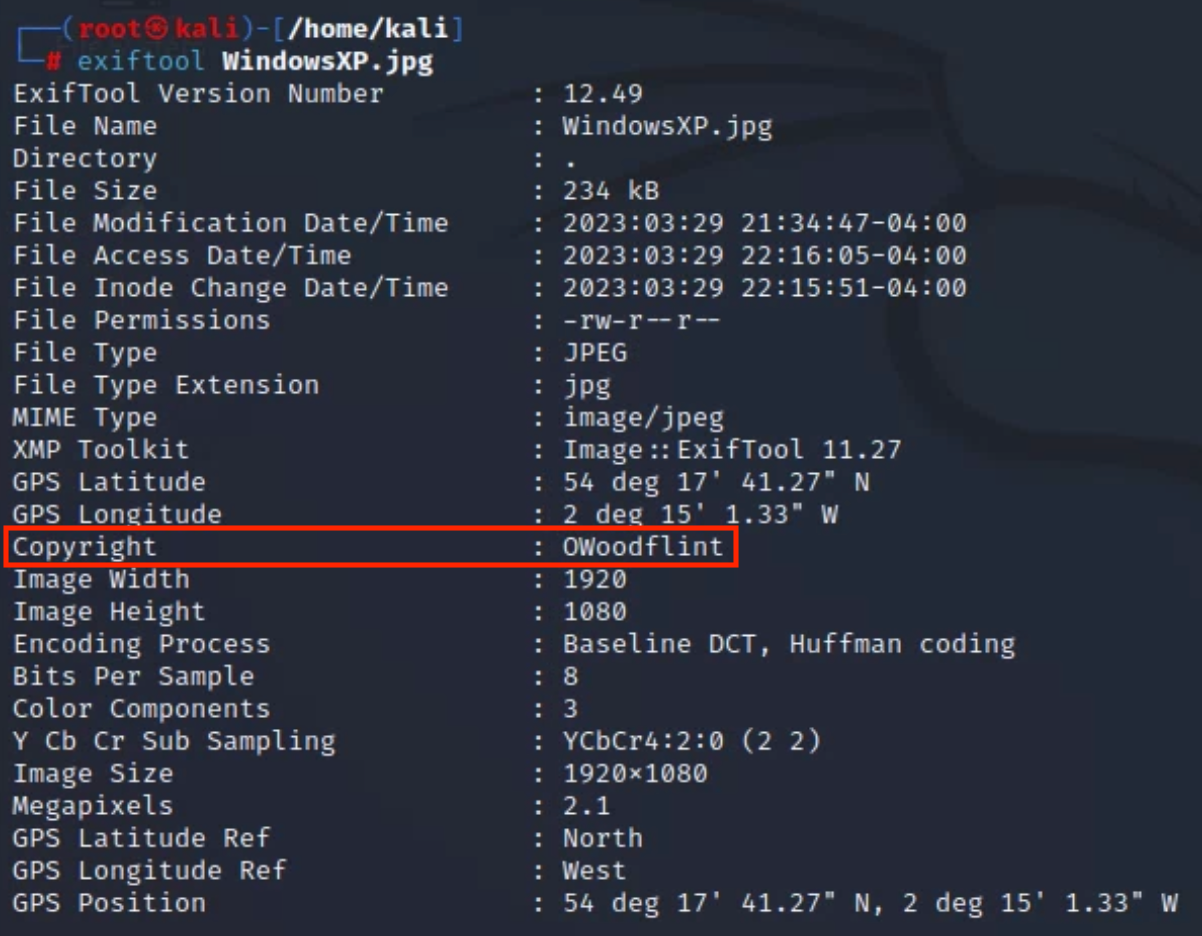
ExifTool shows the metadata of the image contain the information — Copyright: OWoodflint
Part 2: Retrieve the author’s information through Social Engineering
The author’s information gathered from ExifTool provides a starting point for collecting additional information about the background of those involved in creating the image. To begin with, a simple Google search of the author’s name revealed that the author has an associated avatar.

The author's avatar appears on a simple Google search on its name, which first appeared in the image’s metadata
- The users avatar of:
cat
Visit the author’s profile on GitHub and discover their location and email.

The author’s username, city and email are found on a public GitHub repository
- The city that the person was in:
London
- The author’s email address:
OWoodflint@gmail.com
- The site which the author used:
GitHub
Alternatively, the following query can be put to a search engine to identify the author’s footprint on the Internet:
OWoodflint [name] + email

A search query on Google identifies webpages containing an email address starting with the OWoodflint keyword
- Another Google search result shows the author’s latest location:
New York

New York is the keyword
Scraping the source code of the author’s website, an out-of-ordinary value has been located.
- The person’s password:
pennYDr0pper.!

A piece of information is located in the source code of the author’s personal website
Part 3: Use WiGLE API to find out the SSID information from a BSSID
The author gives out the BSSID information on a social media platform. An online Wi-Fi database such as WiGLE can be used to discover more information, such as the potential SSID associated with a BSSID.

A BSSID is obtained from the author’s social media account
curl -i -H ‘Accept:application/json’ -u <API Name>:<API Token> — basic https://api.wigle.net/api/v2/network/detail?netid=**B4:5D:50:AA:86:41** > wifi_tryhackme.json | grep ssid
Ref: https://wigle.net/account

After running the API, the SSID value with “UnileverWiFi” appeared multiple times.
Use jq to parse a JSON and display it in a more readable format.

According to WiGLE’s output parsed by jd, the potential SSID can be located on this key-value pair: “ssid”: “UnileverWiFi”
- The SSID that the author connects to:
UnileverWifi
메타데이터
- post_id
- 5d72049a125a
- slug
- passive-recon-through-exiftool-social-engineering-and-wigle-5d72049a125a
- url
- https://medium.com/@kelvin_ling/passive-recon-through-exiftool-social-engineering-and-wigle-5d72049a125a
- canonical_url
- https://medium.com/@kelvin_ling/passive-recon-through-exiftool-social-engineering-and-wigle-5d72049a125a
- author_url
- https://medium.com/@kelvin_ling
- status
- ok
- fetched_at
- 2026-07-25 23:01:09




