Active Directory Pentesting in 2026: Why It Still Matters and How to Master It.
Identity remains the battlefield. Active Directory remains the terrain. Knowing it well is no longer optional.
Active Directory Pentesting in 2026: Why It Still Matters and How to Master It.
Identity remains the battlefield. Active Directory remains the terrain. Knowing it well is no longer optional.
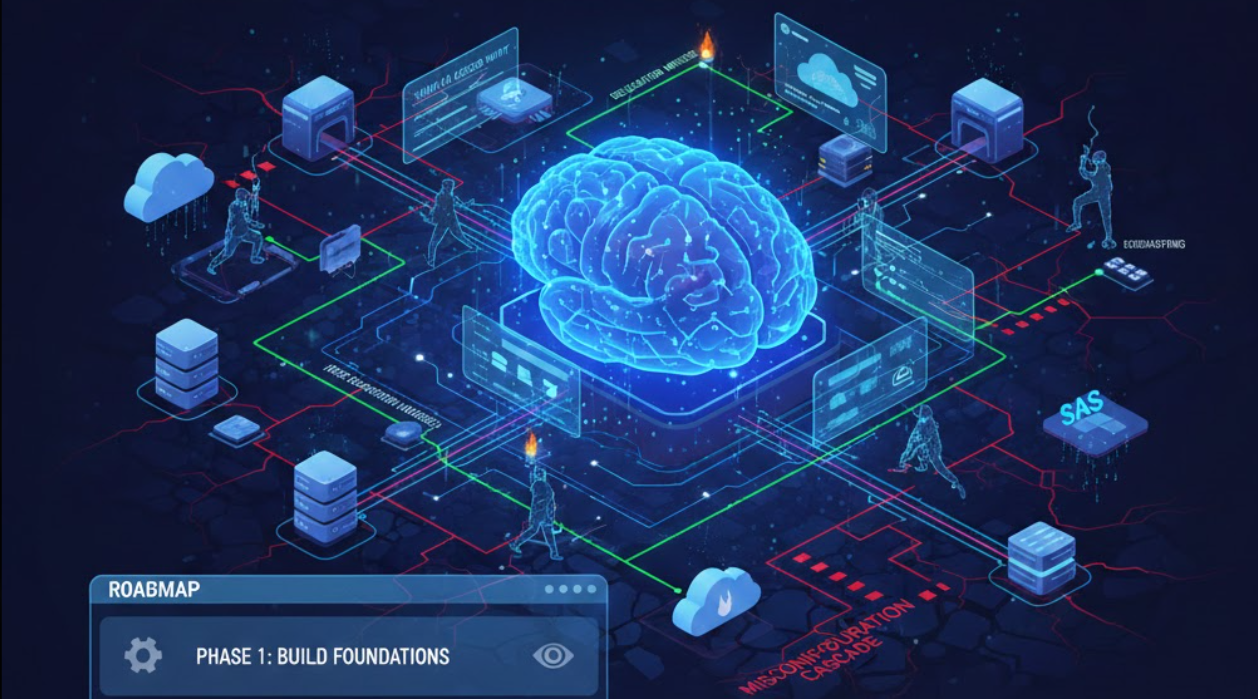
AD Environment
Despite the rapid shift toward cloud-first strategies, identity-as-a-service platforms, and zero-trust models, Active Directory remains the control plane of most enterprise environments. In 2026, it is still the system that determines who can access what, where trust exists, and how far an attacker can move once inside a network.
For security professionals, this reality creates a clear opportunity. Active Directory pentesting is not a legacy niche. It is one of the most practical and high-impact skills you can develop today. Understanding how AD fails, how it is abused, and how compromises unfold is what separates surface-level testing from meaningful security work.
This article explains why Active Directory pentesting remains critical and provides concrete attack examples and a structured roadmap to help you build real competence rather than just theoretical knowledge.
Why Active Directory Still Drives Enterprise Breaches
Most modern organizations operate hybrid environments. On-premises Active Directory coexists with Entra ID, cloud workloads, SaaS platforms, VPNs, and internal applications. While defenses around endpoints and perimeters continue to improve, identity remains the weakest and most exploited layer.
Active Directory sits at the center of this identity ecosystem. File servers, email systems, administrative tools, and even cloud roles often inherit trust directly or indirectly from AD. When AD is misconfigured, the impact is rarely limited. A single weakness often cascades into full domain or tenant compromise.
Attackers understand this dynamic well. Rather than burning exploits, they rely on legitimate features such as delegation, group memberships, and authentication flows. These attacks blend into normal operations, making them difficult to detect and devastating when successful.
For pentesters, this means one thing. If you do not test Active Directory thoroughly, you are not testing the environment realistically.
Real Active Directory Attack Examples Seen in the Wild
Active Directory pentesting becomes valuable when it reflects how real attackers operate. The following examples represent common paths to compromise in enterprise networks.
Credential Exposure Leading to Domain Access
An attacker gains access to a single workstation through phishing or a vulnerable internal application. Domain credentials are reused locally or exposed in memory. With valid credentials, the attacker authenticates across the network, enumerates permissions, and begins mapping privilege relationships.
This scenario appears frequently because most organizations underestimate how dangerous valid credentials are. No exploit is needed, only poor hygiene.
Kerberoasting and Service Account Abuse
A low-privileged domain user requests Kerberos service tickets associated with service accounts. Weak or unrotated passwords allow offline cracking. Once compromised, these service accounts often grant access far beyond their intended scope.
This attack highlights why service account management is a critical AD security issue rather than an administrative inconvenience.
Permission and Delegation Misuse
In many environments, users or groups are granted excessive permissions on directory objects. These permissions allow attackers to modify group memberships, reset passwords, or alter Group Policy Objects.
Nothing crashes. No alerts fire. The attacker simply uses Active Directory as designed, escalating privileges through trust relationships that were never reviewed.
Replication Abuse and Full Domain Compromise
Replication privileges are sometimes assigned too broadly. An attacker with these permissions can request credential data for all domain accounts. At this stage, the environment is effectively lost.
This type of failure demonstrates why Active Directory compromise often results in total organizational impact.
Hybrid Escalation from AD to Cloud
On-prem AD is commonly synced with cloud identity platforms. Once AD is compromised, attackers abuse synchronization or federation trust to access cloud resources.
In hybrid environments, on-prem compromise is often the fastest route to cloud dominance.
What Active Directory Pentesting Teaches That Other Testing Does Not
Active Directory pentesting forces you to think beyond vulnerabilities. You learn to reason about trust, inheritance, and privilege flow. You begin to see security failures as systems problems rather than isolated flaws.
This mindset improves how you approach:
- Network and identity architecture
- Incident response and breach analysis
- Defensive design and access control reviews
Even for blue team professionals, understanding AD attack paths changes how you interpret logs, alerts, and risk.
A Step-by-Step Roadmap to Master Active Directory Pentesting
Learning Active Directory effectively requires structure. The roadmap below focuses on depth and practical understanding rather than tool memorization.
Phase 1: Build the Foundations
Learn how domains, forests, trusts, and organizational units work. Understand authentication flows and why Kerberos behaves the way it does. Build a small lab and break it repeatedly.
Outcome: You stop guessing and start reasoning.
Phase 2: Gain Visibility Through Enumeration
Learn how attackers enumerate users, groups, permissions, and relationships. Understand what attack paths represent and how privilege is inherited.
Outcome: You recognize risk hidden in plain sight.
Phase 3: Understand Credential-Based Attacks
Study how credentials are exposed, reused, and abused. Practice realistic password attacks and service account exploitation.
Outcome: You understand why credential security determines breach outcomes.
Phase 4: Practice Privilege Escalation and Movement
Abuse permissions instead of exploits. Move laterally using legitimate mechanisms. Escalate quietly.
Outcome: You learn how real attackers operate undetected.
Phase 5: Simulate Domain Compromise
Perform full attack chains from initial access to domain control. Study persistence techniques and post-exploitation impact.
Outcome: You understand the full lifecycle of enterprise breaches.
Phase 6: Learn to Communicate and Defend
Translate attack paths into clear findings. Prioritize issues by business impact. Provide remediation guidance that administrators can realistically apply.
Outcome: You become trusted, not just technical.
Career Value and Long-Term Relevance
Active Directory expertise consistently opens doors. Identity security is now a board-level concern, and professionals who understand AD deeply are pulled into red teaming, incident response, internal security engineering, and advisory roles.
As automation handles basic scanning, human insight becomes more valuable. AD pentesting rewards understanding, judgment, and experience. These traits do not age out.
Closing Thoughts
In 2026, Active Directory is not legacy infrastructure. It is the backbone of enterprise trust. When it fails, everything fails with it.
Mastering Active Directory pentesting is not about chasing trends. It is about learning how real environments are compromised and how meaningful security is built.
Identity remains the battlefield. Active Directory remains the terrain. Knowing it well is no longer optional.
Top Platforms to Learn AD Pentesting in 2026
Hack The Box | TCM Security Academy | Hack Smarter | Try Hack Me
References
- Microsoft Corporation. Active Directory Domain Services Overview. Microsoft Learn. Available via Microsoft official documentation.
- Microsoft Corporation. Microsoft Entra ID Architecture and Hybrid Identity Design. Microsoft Learn.
- MITRE ATT&CK Framework. Enterprise ATT&CK Techniques Related to Active Directory. MITRE Corporation.
- SpecterOps. Attack Path Management and Active Directory Security. SpecterOps Whitepapers and Research Blog.
- Harmj0y and Andy Robbins. BloodHound: Six Degrees of Domain Admin. Black Hat USA Briefings.
- NIST. SP 800–53 Security and Privacy Controls for Information Systems and Organizations. National Institute of Standards and Technology.
- NIST. SP 800–61 Revision 2 Computer Security Incident Handling Guide. National Institute of Standards and Technology.
- ENISA. Threat Landscape for Identity and Access Management Attacks. European Union Agency for Cybersecurity.
- CrowdStrike. Global Threat Report 2025. CrowdStrike Intelligence.
- Mandiant. M-Trends 2025 Special Report. Google Cloud Security.
- Microsoft Security Response Center. Kerberos Authentication Technical Reference. Microsoft.
- Harmj0y. Abusing Active Directory Permissions and Delegation. SpecterOps Research.
- Sean Metcalf. Active Directory Security Best Practices. ADSecurity.org.
- Verizon. Data Breach Investigations Report 2025. Verizon Business.
- Gartner. Identity as the New Security Perimeter. Gartner Research Notes.
- ISO. ISO IEC 27001 Information Security Management Systems. International Organization for Standardization.
#CyberSecurityCareers hashtag #Pentester hashtag #RedTeaming hashtag #SecurityEngineering hashtag#ThreatResearch hashtag #SecurityResearch hashtag #InformationSecurity hashtag #CyberDefense hashtag #IAM hashtag #NetworkSecurity hashtag #ZeroTrust hashtag #HybridIdentity hashtag #CloudSecurity hashtag #MicrosoftEntra hashtag #EnterpriseIT
메타데이터
- post_id
- 8341ac9706a2
- slug
- active-directory-pentesting-in-2026-why-it-still-matters-and-how-to-master-it-8341ac9706a2
- url
- https://systemweakness.com/active-directory-pentesting-in-2026-why-it-still-matters-and-how-to-master-it-8341ac9706a2
- canonical_url
- https://systemweakness.com/active-directory-pentesting-in-2026-why-it-still-matters-and-how-to-master-it-8341ac9706a2
- author_url
- https://medium.com/@99alibinazam
- status
- ok
- fetched_at
- 2026-07-20 03:20:25