Speeding up the RMF Pipeline Through Proper Automation
RMF can be tedious, drawn out, paper heavy, and disjointed. It does not have to be. We explain how Soteria Software was born to solve that.
Speeding up the RMF Pipeline Through Proper Automation
RMF can be tedious, drawn out, paper heavy, and disjointed. It does not have to be. We explain how Soteria Software was born to help solve this problem. Now and into the future.

Automating data pipelines and processes to gain truthful approval faster
Current Challenges with most RMF Pipelines
Using the Risk Management Framework to track your cyber compliance is required in US Federal spaces. Whether you are an agency, a contractor, a vendor, or an integrator you have seen RMF in your lifetime. And for a lot of groups we have talked to, they are still stuck in the old manual ways to do this.
At Soteria Software, our two founders (me being one of them) have done this for over 20 years, starting with DITSCAP and then DIACAP and now RMF. And we saw it done manually from 2004 onward when we were just getting into cyber compliance heavy. Some groups are still doing the same manual processes today.
Back in 2015, after seeing this over and over at different companies and agencies, we made a commitment to automate this as much as possible. Soteria Software was born 5 years ago from that commitment.
Regardless of the compliance acronym, there were problems then that still exist today implementing RMF that are commonly shared:
- it is disjointed with manual files and process across disparate teams
- it is complex, with most people involved only knowing their small part
- you have to track compliance of technology as well as process/policy
- you have to track patches of software, operating systems, and more
- you need to know the current state, plan to fix, and mitigate what you can
- the bottom line is proper risk mitigation, on tech as well as process and policy
The goal through this process is your ATO, Authority to Operate. That is not the “end goal” though. At least it should not be. It is part of the continuous process on cyber compliance, that leads to cyber hygiene and proper cyber security.
Several of the main challenges with RMF are the ones listed above. At Soteria Software, the solution we believe at least in part is proper automation toward tracking all this data truthfully. And showing proof if it. While driving decisions from it, manually and automatically.
And doing this while a feedback loop validates compliance from cyber hygiene and cyber security. Or fixes it and adjusts going forward continuously.
How we work towards solving this
There is no one company, speaker, vendor, or technology that solves this all in one fell swoop. If they tell you that, they are lying. Run away fast.
However, there are groups, vendors, and technology that can work together to get closer to a continuous ATO process for RMF and other frameworks. As long as they are not creating yet another data silo.
We are one of them. And we are working with partners like RapidFort and Elastic to automate and secure from day 1 onward.
The way we are working toward increasing the speed, trust, and validity of RMF and cyber compliance is through proper automation where it fits best. First using our OpenRMF Professional solution to get all the data into a single pane of glass. And working toward these first automation steps:
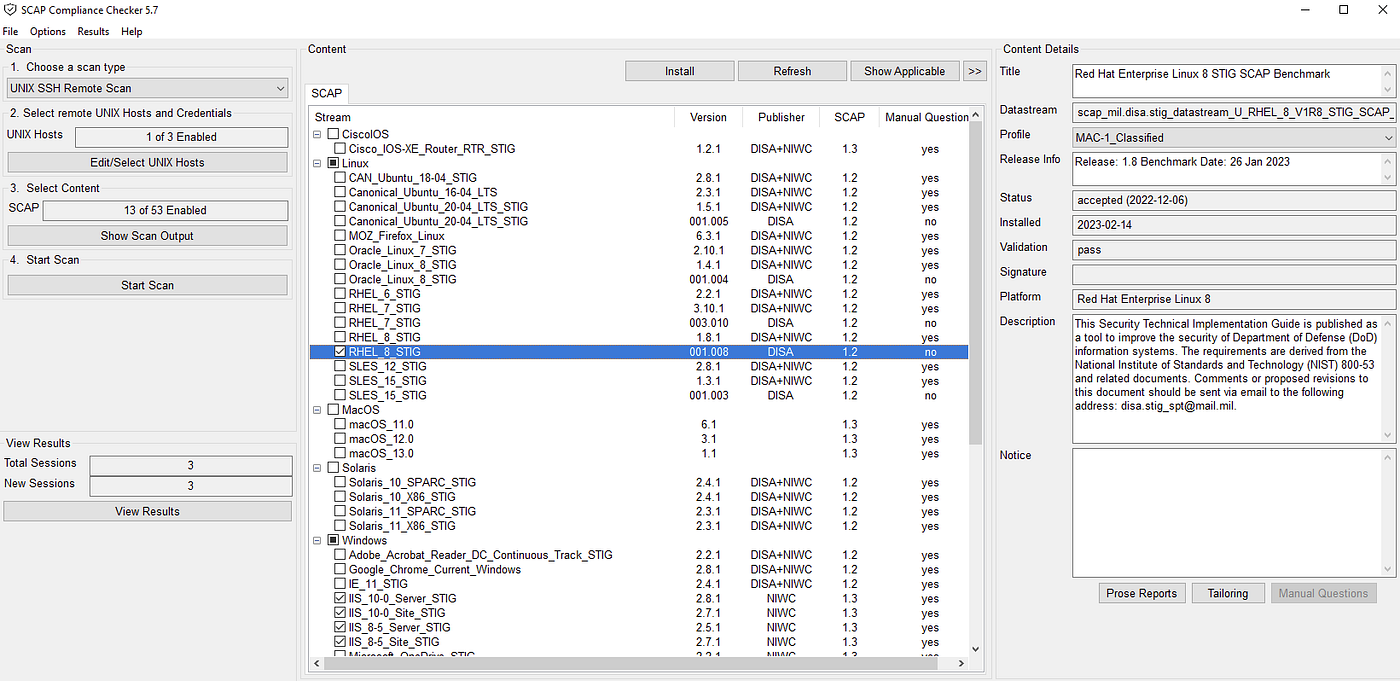
- Ingesting common types of scan data you already do (SCAP, Audit Compliance, checklists, patch vulnerability, container scans, software scans), and tracking trends and history over time
- Ingesting compliance statements for process and policy
- Tracking evidence to prove compliance
- Correlating all this automatically to a live Plan of Action and Milestones (POAM) and tracking history over time
- Generating compliance against all this data over time, and showing comparisons, history, and trends
- Using a team collaborative environment with roles and permissions for least privilege
- Generating artifacts that go into current US Federal programs of record for tracking ATOs easily

OpenRMF Professional ATO Dashboard with your latest information
You can see this in action at our website or using our live demo.
It is one thing to read about it. It is an entirely different experience seeing it firsthand. You can even download and evaluate what we are saying for yourselves with your own eyes, hands and data.
What is next up for our RMF Pipeline view
If using OpenRMF Professional is one of the first steps, what is after that? More sensible automation and decision making where it fits and makes sense for your organization and use cases.
Currently, we are using RapidFort to harden our images and software as well as scan our images to show compliance at our software component level. That is one more layer to add in early on for any software group.
We also are working with Elastic on using and integrating with their Elastic SIEM product. We have a whole list of videos showing our progress out in the open for you to see here. This allows tracking compliance, proving it is correct or not, and aids your team in fixing issues and tightening security. Which impacts compliance directly.
We are also using Elastic to build AI Agent searching for conversations you can have with your data interactively. And then building on top of that to process information correctly, alert smartly where necessary, and adjust compliance on your systems directly based on the SIEM data to show true compliance.
Your team uses all this information to drive decision making. You learn the heartbeat of your systems in a structured way. Know when something needs fixing. Understand your compliance across all teams in real time or near real time. You better understand your security posture and current risk as well.
And your team adjusts your infrastructure, boundaries, rules, policies, and the requirements based on your needs and required security and risk mitigations. And does this as much as possible through automation, using human intervention and automating fixes as you learn and go forward.
We are also working with a Navy group to automate data into and out of eMASS directly to allow these processes to run even faster. With proper, truthful data built from automated scans, SIEM integration, and team collaboration.
Where that leads you
This leads to a proper automated cyber compliance process that teams can feed, use, and learn from to adapt as things change over time. And can repeat over and over, adjusting the tools and processes where appropriate.
Whether it is additional security issues, patches, boundary updates, or different use cases the overarching premise is to have a way to fit these into your automated workflow. Even if only part of this whole process is currently automated while you build the rest.
This allows you to track what is real, not just get a paper document that was outdated months before it was signed as “approved”. It also shows proof to an assessor what you have done, what you are doing, and how you can proactively act in the future toward better cyber security.
And in todays’ time of contract language, legal language, and even state / federal / international laws it shows you are doing your due diligence to not only be compliant. It shows you working to be as secure as possible as well, while continually learning how to do that better.
What to do next
First, see how OpenRMF Professional for you and your team gets your automation going using the scans and data you already have now. Get a demo or download and evaluate for yourself. And see how our quick setup, video training, and simple pricing let you get started quickly with your own personnel.
If you are doing software development, see how solutions such as RapidFort can help secure your software from day 1.
Also check out Ansible, Chef and other automation tools for configuring your operating systems and devices securely from the outset.
And see how solutions such as Elastic with their AI Security, SIEM and other features enable a more continuous security process for your organization.
메타데이터
- post_id
- a09b93ff50b4
- slug
- speeding-up-the-rmf-pipeline-through-proper-automation-a09b93ff50b4
- url
- https://medium.com/@dale-bingham-soteriasoftware/speeding-up-the-rmf-pipeline-through-proper-automation-a09b93ff50b4
- canonical_url
- https://medium.com/@dale-bingham-soteriasoftware/speeding-up-the-rmf-pipeline-through-proper-automation-a09b93ff50b4
- author_url
- https://medium.com/@dale-bingham-soteriasoftware
- status
- ok
- fetched_at
- 2026-06-13 07:35:29