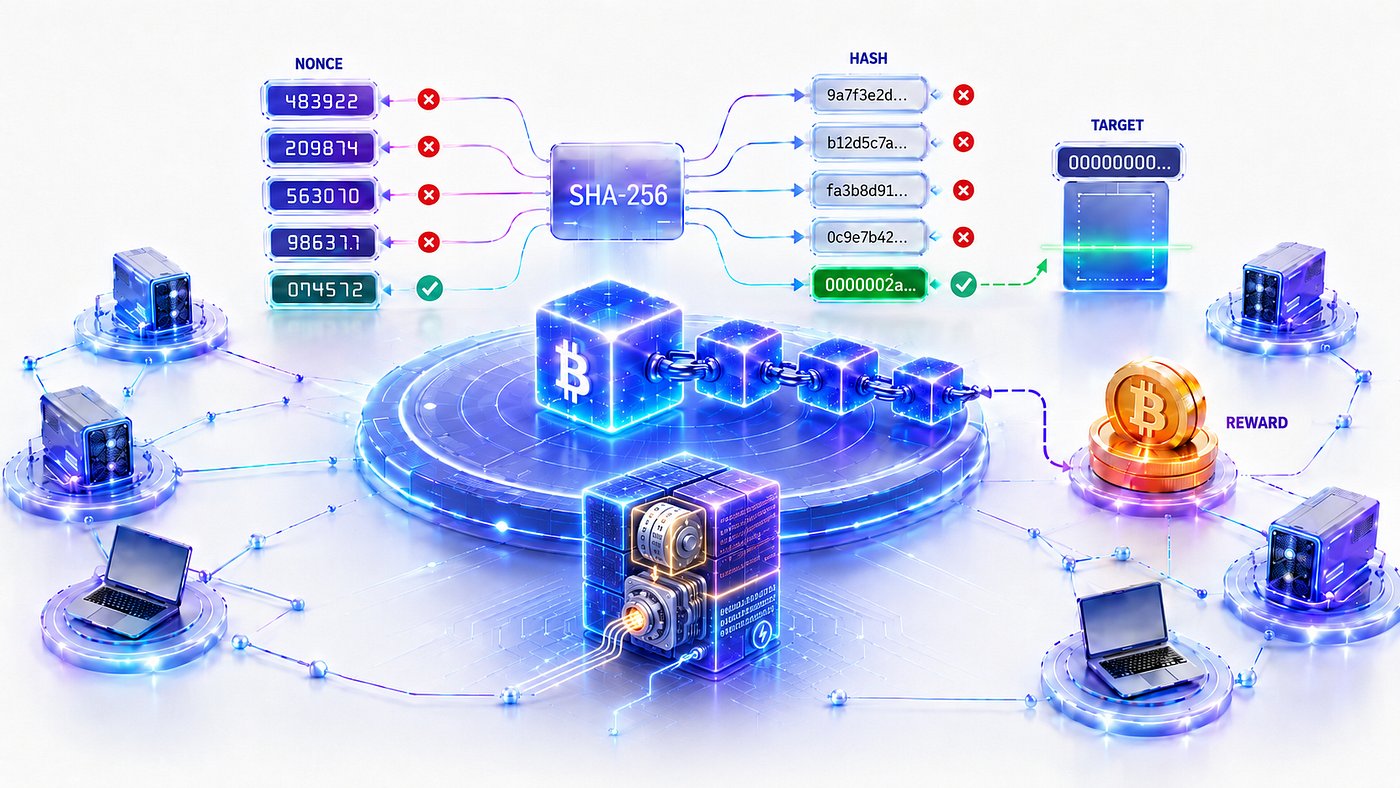
Blockchain under the Hood: P2P Networks, Cryptography, Consensus, and Proof of Work — Part 2 of 4
One of the most fascinating aspects of blockchain is how it brings together ideas from multiple disciplines — computer science, distributed…
Blockchain under the Hood: P2P Networks, Cryptography, Consensus, and Proof of Work — Part 2 of 4
One of the most fascinating aspects of blockchain is how it brings together ideas from multiple disciplines — computer science, distributed systems, cryptography, economics, and even game theory — and assembles them into a single, powerful framework.

This is Part 2 of a four-part series, Blockchain under the Hood, where we peel back the layers and understand how blockchain actually works — from its data structures and cryptography to networking and consensus:
- Part 1: What is Blockchain? + Hash Cryptography Read here
- Part 2: Immutable Ledger + Distributed P2P Network (you’re here)
- Part 3: How Mining Works Read here
- Part 4: Consensus Protocols Read here
In Part 1, we explored what blockchain is and dove deep into hash cryptography — the mathematical foundation that makes blockchain possible. We saw how cryptographic hash functions create unique digital fingerprints for data, and how these fingerprints are used to link blocks together.
But here’s the thing: just linking blocks with cryptographic hashes isn’t enough to make blockchain secure. If that were all there was to it, blockchain would be vulnerable to attacks in ways that would render it practically useless.
In this part, we’ll uncover the two layers of security that transform blockchain from a clever data structure into an immutable ledger — one that’s practically impossible to tamper with.
The Traditional Ledger Problem
Let’s start with a simple, relatable scenario.
Suppose person A buys a car from person B in exchange for money. Here’s what happens in the traditional system:
- They sign a sale contract or a transfer of ownership document
- This contract gets registered with the Government/Transport Authority
- The government body maintains a ledger/database of all ownership contracts
- In this ledger, the ownership of the car is transferred from B to A
Seems straightforward, right? The ledger entry might say something like:
Person B sold Car #123 to Person A on 2026–01–19
Person A, the new owner, trusts that this central ledger accurately reflects their ownership of the car.
This traditional ledger works… but it has two major weak points:
- First, centralized storage — All the records live in one place — a single database or server. That central server becomes a single point of failure. If it gets hacked, crashes, or if an insider acts maliciously, the integrity of the entire ledger is at risk.
- Second, easy mutability — Entries can be changed or deleted by those who control the ledger. An official could alter the car sale record, or a cybercriminal could break in and modify the database.
Now, suppose an attacker manages to get hold of this database. They could easily modify it, changing the ownership record or even deleting it entirely. Person A would have no means of proving that they own the car or that the sale ever happened. The evidence would simply be… gone.
In our example, Person A’s ownership exists only because the central registry says so. If someone hacked that registry and deleted or changed the entry, Person A’s proof of ownership could vanish. With a centralized, editable ledger, we’re forced to trust that central entity completely — and hope it never fails us.
There are usually safeguards and backups in place, but the possibility of tampering or human error is always there.
Data in a traditional ledger is only as secure as the authority (and infrastructure) maintaining it.
Blockchain’s Solution: An Immutable Ledger
This is precisely the problem blockchain was invented to solve — the problems of centralization and mutability.
At its core, a blockchain is a distributed ledger that is append-only. You can add data, but you cannot change or delete what’s already there.
How does it achieve this? By structuring the ledger into blocks of data that are cryptographically linked together, forming a chain. This clever structure makes the ledger effectively immutable — meaning once data is recorded and confirmed, it’s extremely difficult to alter or remove.
Immutability: In the context of blockchain, immutability means that once data is recorded on the ledger and confirmed by the network, it cannot be altered or deleted. The record is permanent. Any attempt to change historical data will be detected (due to broken cryptographic links) and rejected by the system, making the ledger tamper-proof.
How Blockchain Helps in the Car Ownership Scenario?
Now, suppose the Government/Transport Authority used blockchain to store records.
Each block contains ownership records for one car (or asset). The ownership transfer from B to A gets stored in a new block, which is then added to the chain. Over time, as more ownership records are added, the blockchain grows longer.

Now, here’s where things get interesting.
When an Attacker Tries to Modify Data
Let’s say an attacker wants to modify the information in one of the blocks — perhaps trying to undo Person A’s car purchase. Here’s what happens:
Step 1: Data Change — The moment they modify the data in the block, the hash of that block changes. Remember from Part 1 — even a tiny change completely alters the hash value.
Step 2: Hash Mismatch — The next block in the chain still contains the original hash of the modified block (the “previous hash” that was recorded when that next block was added). Now the modified block’s new hash doesn’t match what the next block expects.
Step 3: Link Breaks — The cryptographic link between the modified block and the next block is broken. In effect, the chain is “broken” at that point.
Step 4: Cascading Failure — Because the next block is now invalid (its “previous hash” doesn’t match), the block after that is also invalidated. This failure cascades forward through every subsequent block. One tweak in a single block has unraveled the integrity of all blocks that came after it.
Step 5: Network Rejection — The blockchain network, which constantly checks the validity of blocks, will see that something is wrong. The hashes don’t line up. As a result, the network rejects the tampered block and any blocks after it. The attacker’s altered version of the ledger is simply not accepted as truth.

And thus, the blockchain becomes INVALID.
The Validation Software
If the Government/Transport Authority were to adopt this blockchain system, they’d need software that continuously monitors the chain for validity.
The beauty of blockchain lies in the fact that it is super easy and quick to validate it. We just have to match the hash of the current block with the “previous hash” value of the next block. Since the blocks are cryptographically linked, this check can be performed in milliseconds.
Any modification or tampering of the data in any of the blocks will result in the blockchain being INVALID due to the mismatch of hash and “previous hash” values.
But here’s the catch — while this makes detecting tampering easy, it doesn’t necessarily prevent a determined attacker.
The Mining Obstacle
First off, if the attacker wants to modify data in any block, they’ll have to mine that block.
Mining a block is not easy at all. It is similar to solving a cryptographic puzzle — which is extremely time-consuming. We’ll explore the mechanics of mining in detail in Part 3, but for now, understand that it requires significant computational work.
Even if the attacker somehow manages to mine the modified block, they’d still need to mine all the future blocks in the chain as well. Otherwise, the blockchain would remain invalid, and the tampering would be immediately obvious.
In most blockchain systems (like Bitcoin), blocks are secured by heavy computational work (Proof of Work mining). Re-mining a long sequence of blocks is astronomically difficult. Recomputing all subsequent blocks would require enormous computing power — essentially an impractical amount for any single adversary.
But let’s say the attacker is adamant and somehow possesses enormous computational resources. They manage to mine not just the modified block, but also all the future blocks in the chain. The blockchain would appear valid again.
This is where blockchain’s second layer of security comes into play: the distributed P2P network.
A Network of Peers: Distributed P2P Network
As we saw previously, by virtue of design, a blockchain has a layer of security in it — the blocks are cryptographically linked with each other. Any modification of the data in any of the blocks will result in the blockchain being INVALID.
However, this requires validation software to be run on the blockchain continuously, which keeps monitoring and validating the chain.
This alone might not be sufficient to guarantee the security of the blockchain. As we just discussed, if the attacker managed to mine the modified block and all the future blocks in the chain, the validation checks will not be able to capture this. The blockchain will stand at risk of being attacked.
Thus, to add an additional layer of security to the blockchain, a distributed P2P network is set up.
How the P2P Network Works
Blockchains eliminate the need for a central server by leveraging a distributed peer-to-peer (P2P) network of nodes.
Peer-to-Peer (P2P) Network: A decentralized network where each node (participant computer) directly connects and shares data with others rather than through a central server. In a blockchain’s P2P network, every node holds a copy of the ledger and updates it in coordination with other nodes.
Think of it this way: instead of the ledger sitting on one company’s server, it lives on thousands of computers around the world.
Here’s how it works:
- All nodes/computers in the network speak the same language and agree upon certain rules/protocols (called the consensus protocol)
- These nodes need not be in proximity to each other — they can be distributed as geographically apart as they like
- Joining the network is easy — nodes just have to download a piece of software and agree upon certain rules/protocols
- Every node maintains the SAME copy of the blockchain

The main idea behind setting up a P2P network is that all nodes in the network will maintain ONE UNIFIED version of the blockchain. The idea is pretty much similar to having a distributed version control system through Git.
Every time a new block of transactions is created, it’s broadcast to all those computers. They verify it and add it to their own copy of the chain. In this way, all copies of the ledger remain identical.
Any block modified or any new block added to the chain should be communicated across to all nodes, and all their respective local copies of the blockchain must be updated.
This distributed P2P network is the mechanism by which an untrusted environment is turned into a trusted one.
These distributed P2P networks can be of two types:
- PERMISSIONED — Here, the number of nodes is locked, and not everyone can join the network. Think of private blockchain networks used within organizations.
- PERMISSIONLESS — Here, anyone can join and be part of the network. This is how Bitcoin and most public blockchains operate.
The Second Layer of Security
This decentralization yields a powerful advantage: there’s no single point of failure. No single corrupted official or hacked server can compromise the ledger, because dozens or thousands of other nodes will immediately detect inconsistencies.
It’s like a village where everyone keeps a copy of the town’s transaction log. If Person A buys Person B’s car, all villagers write it down in their notebooks. If one person tries to cheat later and erase the entry in their notebook, it won’t match what everyone else has. The group will reject that false record because the consensus of everyone else tells them the truth.
The blockchain works in a similar communal way — trust is placed in the network’s collective agreement rather than in a single authority.
How Distribution Provides Security
Due to the distributed P2P network, any modification or addition to the blockchain is communicated to all other nodes in the network.
This offers a direct benefit in terms of recoverability — if data in one of the nodes is damaged or lost, it can easily be recovered since all nodes maintain ONE UNIFIED version.

Now let’s imagine the worst-case attack scenario:
An attacker attacks one of the nodes and tries to change data in one of the blocks. Let’s assume they’re able to somehow mine the malicious block plus all future blocks of the chain. This means they have somehow managed to breach the first layer of security — the cryptographic linking of blocks.
Here’s what happens next:
Step 1: Nodes Communicate — Since nodes are interconnected, they’ll communicate with each other about their local copies of the blockchain.
Step 2: Inconsistency Detected — They’ll find that one of the nodes (which the attacker attacked) has a different copy of the blockchain than the rest of the nodes in the network.
Step 3: Majority Rules — The other nodes will immediately know that their copy is the correct one, because they’re in the majority. And the majority wins elections, let alone a blockchain!
Step 4: Forced Update — As a result, the attacked node will have to change its version of the blockchain in order for everyone in the network to have ONE UNIFIED version of the blockchain. Not doing so would result in that node being thrown out of the network for being malicious or not obeying the protocols.

Therefore, the distributed P2P network provides a second layer of defense due to the interconnectivity among nodes.
Because every node has the complete ledger, redundancy is built in. Even if a portion of the network goes down, the blockchain remains available and intact through other nodes. And because each node independently verifies new transactions and blocks, participants don’t have to blindly trust any single source.
In blockchain lingo, the system is often called trustless — not because there’s no trust, but because trust is placed in math, cryptography, and the consensus of many participants rather than any single party.
Network Consensus: Agreeing on One Truth
When you have many independent nodes, they need a way to agree on what the “official” ledger is. They must reach an agreement on which new block gets added next, especially when multiple nodes may propose different blocks simultaneously.
This is where blockchain introduces a consensus protocol.
Consensus Protocol: A set of rules and processes by which a decentralized network comes to agreement on the state of the ledger. In blockchain, a consensus protocol (such as Proof of Work or Proof of Stake) ensures that all honest nodes agree on which transactions and blocks are valid, and it keeps the ledger consistent across the network.
The consensus protocol is like a democratic process that the nodes follow to pick the next valid block and reject invalid ones. Different blockchains use different methods — Proof of Work as used in Bitcoin (where nodes compete via computing power), or Proof of Stake as used in newer systems (where nodes vote based on staked tokens). We’ll explore these in more detail in Part 4.
But the goal is the same: only one chain of blocks is accepted as the true ledger, and everyone converges on that chain. If any node’s copy deviates (due to error or malicious intent), the consensus rules ensure that the copy is ignored in favor of the majority-approved chain.

All the nodes could be situated miles apart from each other, and none of them can trust any of the other nodes to be genuine or to have the correct version of the blockchain. However, by the mechanism of a distributed P2P network, we can turn an untrusted environment into a trusted one!
Because we may not trust any individual node to have the correct version of the blockchain, but we do trust the protocols and cryptography that govern this mechanism. Thus, the whole mechanism of the distributed P2P network guarantees trustworthiness as opposed to any single node being trustworthy or not.
And this trust — brought about by each node’s commitment to consensus protocols — is what makes the whole system work in harmony.
Securing the Network: The 51% Attack
You might be wondering: what if someone tries to cheat the system by exploiting the network itself? Could a group of attackers coordinate to add a fake block or alter the ledger across all nodes?
Blockchain’s defense here is the sheer scale and unified rules of the network. An attack would have to overpower most of the honest nodes at once, which is extraordinarily difficult.
What is a 51% Attack?
Theoretically, the only way for an attacker to be successful in modifying data in a blockchain is to mine the malicious block plus all future blocks in at least 50% of the nodes in the network, simultaneously.
Imagine: if we have 1 million nodes in the network, the attacker would have to simultaneously mine multiple blocks on at least 500,000 nodes. And all of these nodes can be sitting miles apart geographically, so there will also be delays due to transmission time.
In blockchain terms, an attacker would need to control over 50% of the network’s total computing power (in Proof of Work) or stake (in Proof of Stake) to have any shot at forcing a different version of the ledger. This scenario is known as a 51% attack.

How a 51% Attack Would Play Out
Here’s how it might work in a Proof of Work blockchain like Bitcoin:
- An attacker (or group) gains control of more than half of the total mining hash power
- With this majority, they could secretly mine an alternate chain of blocks — for example, one in which they reverse some transactions or double-spend coins
- Once their alternate chain is longer than the public honest chain (thanks to their superior hash power), they release it to the network
- Because the consensus protocol typically accepts the longest valid chain as truth, the network would switch to the attacker’s fraudulent chain
- This would let the attacker rewrite history up to a point, possibly stealing assets

Sounds scary, right? But here’s why successful 51% attacks are extremely unlikely on well-established blockchains:
- Enormous Resource Requirement — Gaining majority control of a large network is prohibitively expensive and difficult. The Bitcoin network, for instance, is secured by millions of mining machines worldwide. To out-compute all honest miners, an attacker would need a ridiculous amount of hashing power and electricity, costing billions of dollars. For Proof of Stake systems, an attacker would need to acquire 51% of the total staked currency — often an unfeasible amount of money (and buying that much would drive the price up further).
- Detection and Response — Even if an attacker amassed 51% power, maintaining that advantage is hard. The moment they slacken, the honest majority will override them again. Large communities are also on high alert for any signs of such attacks. Exchanges and users can take defensive actions (like pausing transactions) if an attack is detected.
- No Reward, High Risk — The economic incentive to carry out such an attack is low. The value of a cryptocurrency might plummet if its network is compromised, meaning the attacker could end up spending a fortune to control the network only to destroy the very value they might gain. It’s like winning a pyrrhic victory — costly and self-defeating.
Imagining the complexity and effort required, practically doing this is next to impossible for any attacker.
In practice, 51% attacks have been observed only on smaller blockchains with limited miners or stakers. Major public blockchains (Bitcoin, Ethereum, etc.) are so large that coordinating over half of the network power is virtually impossible with today’s technology and resources.
This is why decentralization (many distributed participants) directly contributes to security: the more participants, the harder it is for any one group to seize majority control.
The Price Paid for Turning an Untrusted Environment into a Trusted One
From an efficiency standpoint, this mechanism of a distributed P2P network, combined with the cost of continuously validating the blockchain, is extremely inefficient.
It would have been much cheaper if the storage and validation of the blockchain were centralized to just one node. Less hardware, less electricity, less network bandwidth consumed.
However, this extra effort spent is the cost paid to turn an untrusted environment into a trusted one.
All the nodes could be situated miles apart from each other, and none of them can trust any of the other nodes for being genuine or having the correct version of the blockchain. None of them knows who operates the other nodes. They can’t verify the good intentions of other participants.
Yet, through this distributed P2P network, trust emerges — not from trusting individual nodes, but from trusting the protocols and cryptography that govern the system.
We don’t trust the nodes; we trust the mechanism.
And this trust — brought about by each node’s commitment to consensus protocols — is what makes the whole system work in harmony.
Two Layers of Security: The Complete Picture
We can now fully appreciate the beauty of the design of blockchain, which makes it impossible to modify or tamper with the data in it because of its two layers of security:
Layer 1: Cryptographic Hash Links (Immutable Ledger) — The blocks are linked to one another using cryptographic hashes. This makes the ledger tamper-evident and tamper-proof — once data is in the blockchain, altering it would break the chain and require an impractical amount of recomputation. Any modification to a block’s data changes its hash, which breaks the cryptographic link with the next block, cascading through all future blocks and making the blockchain invalid.
Layer 2: Distributed Consensus (P2P Network) — The copies of the blockchain are available to all the nodes in the network. The ledger is maintained by a distributed network of nodes that must all agree on additions via a consensus protocol. There is no central point to attack or corrupt. An adversary would need to subvert the majority of the network to falsify the ledger, which, for large networks, is effectively infeasible.
Together, these layers mean that blockchain networks can be open and “trustless” yet highly secure. Data on the blockchain is locked down by math and consensus, not by the decree of any one institution.
In our car sale example, Person A doesn’t have to trust a single registry. Instead, they trust that thousands of nodes and cryptographic mechanisms together will defend the truth of their ownership record.
Thus, having a blockchain covers both our points of failure from traditional ledgers:
- Having records in one central location — mitigated by the distributed P2P network
- Ability to change data easily — mitigated by cryptographic linking and the consensus protocol
Wrapping Up Part 2
In the second part, we’ve explored how blockchains achieve an immutable ledger through cryptographic linking and how the distributed P2P network creates a second layer of security. But there’s still a piece missing from this puzzle.
We’ve mentioned “mining” several times as a barrier to tampering. We’ve referenced “consensus protocols” that govern how nodes agree on the state of the blockchain.
But how exactly does mining work? What makes it so computationally difficult? What is Proof of Work, and why is it central to blockchain security?
These are the questions we’ll answer in Parts 3 and 4 of this series, where we’ll dive deep into the mining process — understanding nonces, difficulty adjustment, and the cryptographic puzzles that miners must solve.
Stay tuned with the next installment as we continue peeling back the layers of Blockchain under the Hood!
- Part 1: What is Blockchain? + Hash Cryptography Read here
- Part 2: Immutable Ledger + Distributed P2P Network (you’re here)
- Part 3: How Mining Works Read here
- Part 4: Consensus Protocols Read here
If you found this helpful, you’re welcome to follow along here or connect with me on LinkedIn.
메타데이터
- post_id
- b6da2ce58e42
- slug
- blockchain-under-the-hood-p2p-networks-cryptography-consensus-and-proof-of-work-part-2-of-4-b6da2ce58e42
- url
- https://medium.com/@harmeet-singh-bagga/blockchain-under-the-hood-p2p-networks-cryptography-consensus-and-proof-of-work-part-2-of-4-b6da2ce58e42
- canonical_url
- https://medium.com/@harmeet-singh-bagga/blockchain-under-the-hood-p2p-networks-cryptography-consensus-and-proof-of-work-part-2-of-4-b6da2ce58e42
- author_url
- https://medium.com/@harmeet-singh-bagga
- status
- ok
- fetched_at
- 2026-07-09 00:50:33