My OSINT HomeServer (alpha).
I have been during the last few weeks putting together a OSINT server in my homeLab. The main idea is to have a set of tools available at…
My OSINT HomeServer (alpha).
I have been during the last few weeks putting together a OSINT server in my homeLab. The main idea is to have a set of tools available at any time. Now the server is fully functional but it is in an early status. So my idea is to share it in order to gather ideas and feedback.
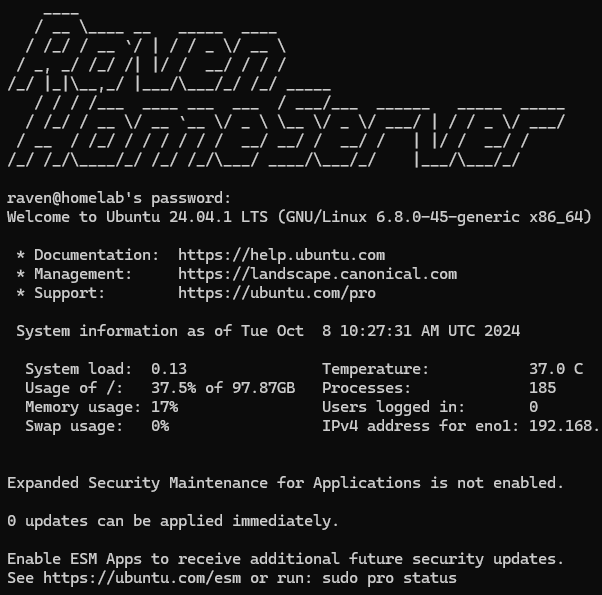
Intro Screen
Hardware
The core of the server is running in a HP Prodesk (4 Cores, 8 Gb RAM, 512 Gb) a basic office desktop computer. It is running Ubuntu Server, although I tried Arch, and other distros…I am still feeling more confortable under debian distros I told about that in this post: https://medium.com/@josejgp/testing-my-new-homelab-427e433f1ca9 .

PIVPN running on a Raspberry pi 4B Argon NEO case with an AMD athlon heatsink
The VPN is outside the the server with the idea of isolation and layered security. It is running on a separete device, both connected to a Switch under a sub-network in my home.

Software
As VPN tunneling I chose WireGuard as is easier and more secure than other solutions. About the tools intalled in the server I have been writting post during the las months about some of them:
-
Spiderfoot. — — — — — — — — — — — — — — - I wrote about Spiderfoot in this post: It is a good tool able to gather OSINT about emails, names, phone numbers. It runs on a webApp and stores all previous searches.
-
Tookie OSINT — — — — — — — — — — — — — — - **In this post** I analysed Tookie not long ago. it’s a tool able to gather OSINT about nicknames across different websites on a CLI
-
Nessus — — — — — — — — — — — — — — - I have also written about Nessus **here**. And even, if this one is not OSINT related, I think it is really usefull in order to improve the hardening of your network. Analyse vulnerabilities of each new endpoint in your network should be a must.
-
Blackwidow, Nikto & Nuclei — — — — — — — — — — — — — — - The Web-server vulnerability scanners trio. I have a post for each of them:
Blackwidow Nuclei and Nikto

table by Gemini
Summary:
- Nikto is great for scanning web servers specifically for vulnerabilities related to outdated software and misconfigurations.
- BlackWidow offers a web crawling capability, making it useful for discovering vulnerabilities by thoroughly inspecting web applications and their dynamic content.
- Nuclei is more of a generalized vulnerability scanner, highly flexible and efficient for a wide variety of environments, thanks to its template-based approach. It’s especially useful in more complex, large-scale environments where automation and customization are required.
- MISP
It is still not fully working due to a problem with Apache
- Shodan — — — — — — — — — — — — — — - Shodan is an amazing earch engine for Internet-connected devices

#!/bin/bash
# Navigate to the Shodan directory
cd ~/tools/shodan
# Activate the virtual environment
source .venv/bin/activate
# Run Shodan CLI
shodan "$@"
# Deactivate the virtual environment after running Shodan
deactivate
This bash is similiar to all the ones used with python tools.
— — — — — — — — — — — — — — -
- PhoneInfoga (Docker)

This tool is similar to Spiderfoot but fully oriented to phone numbers, helping you to gather some basic information and social media connections. The tool is CLI oriented so it makes easier and quicker to use than spiderfoot when the target is just a phone number. Although you can run serve for a Web-client.

In my case this tool is running inside a container, in order to start the tool I am using this bash:
#!/bin/bash
sudo docker run --rm -it sundowndev/phoneinfoga "$@"
And like with the other tools I am using also “alias” to make easier the use of them:
alias msf='msfconsole'
alias phoneinfoga='~/tools/bash_tools/run_phoneinfoga.sh'
alias shodan='~/tools/bash_tools/run_shodan.sh'
alias spiderfoot='/home/raven/tools/bash_tools/run_spiderfoot.sh'
alias tookie='/home/raven/tools/bash_tools/run_tookie.sh'
— — — — — — — — — — — — — — -
- Metasploit Framework
The Metasploit Project is a computer security project that provides information about security vulnerabilities and aids in penetration testing and IDS signature development. It is owned by Boston, Massachusetts-based security company, Rapid7. Wikipedia.
Using the tools in your phone.
Imagine that you need to quickly check some info. How easy would be it with this approach? The answer is quite easy. Using the WireGuard app is easy to access the server from any place.

Then I use Terminus:

An the rest is easy, all tools are working even the web-apps services work fine.

메타데이터
- post_id
- c0783d4f8354
- slug
- my-osint-homeserver-alpha-c0783d4f8354
- url
- https://osintteam.blog/my-osint-homeserver-alpha-c0783d4f8354
- canonical_url
- https://osintteam.blog/my-osint-homeserver-alpha-c0783d4f8354
- author_url
- https://medium.com/@josejgp
- status
- ok
- fetched_at
- 2026-06-14 11:28:49