SQL Injection Attacks Cost Companies $8.7M: Here’s What Every Developer Must Know
SQL injection isn’t a theoretical risk it’s an active threat costing businesses billions annually
SQL Injection Attacks Cost Companies $8.7M: Here’s What Every Developer Must Know
Photo by [NCSE](http://ncse.info/wp-content/uploads/2025/07/sql-injection-login-vulnerability-ncse.webp)
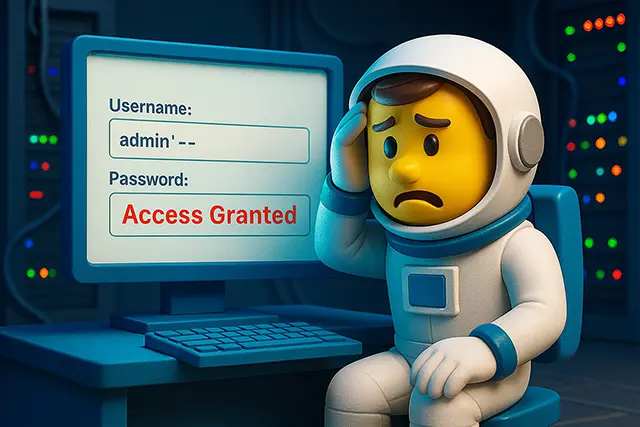

Three months. That’s all it took for a senior developer’s mistake to cost their company 2.4 million customer records and $8.7 million in regulatory fines. The culprit? A single unvalidated input field that made their application vulnerable to SQL injection attacks.
If you think SQL injection is yesterday’s problem, think again. 6.7% of all vulnerabilities discovered in open-source projects in 2024 are SQL injection vulnerabilities while 10% of vulnerabilities discovered in closed-source projects were SQL injection vulnerabilities. Even more shocking: SQL Injection is the main source of web application critical vulnerabilities found globally in 2023, with 23 percent.
The Billion-Dollar Problem That Won’t Go Away
Let me paint you a picture of the current landscape. SQL injection (SQLi) now represents nearly two-thirds (65.1%) of all Web application attacks. That’s not a typo 65.1% of ALL web application attacks.
Recent breaches tell the story better than statistics:
- In 2008, Heartland Payment Systems, a major payment processing company, fell victim to one of the largest data breaches in history due to an SQL Injection attack, with approximately 130 million credit and debit card numbers being compromised
- Sony’s network suffered a severe SQL Injection attack, compromising its digital infrastructure. Around 77 million PlayStation Network accounts were affected, costing Sony an estimated $170 million
- Between November and December 2023, a threat actor successfully stole more than two million email addresses and other personal information from at least 65 websites
Why Developers Keep Making the Same Mistake
Here’s the uncomfortable truth: we know how to prevent SQL injection. We’ve known for over two decades. Yet 29% of web applications are still vulnerable to SQL injections according to recent security reports.
The problem isn’t knowledge — it’s implementation. Consider this vulnerable code that I’ve seen in production more times than I’d like to admit:
// DON'T DO THIS - Vulnerable to SQL injection
app.get('/user/:id', (req, res) => {
    const query = `SELECT * FROM users WHERE id = ${req.params.id}`;
    db.query(query, (err, result) => {
        res.json(result);
    });
});
An attacker could simply navigate to /user/1 OR 1=1 and potentially dump your entire user table. It's that simple, and that devastating.
The Real Cost of SQL Injection in 2025
The average cost of a data breach was $4.88 million in 2024, the highest average on record. But the true cost extends beyond immediate financial damage:
- Regulatory Fines: GDPR can impose fines up to 4% of annual global turnover
- Legal Costs: Class-action lawsuits from affected customers
- Reputation Damage: Customer trust takes years to build, seconds to destroy
- Operational Disruption: Average breach lifecycle is 292 days from identification to containment
Three Simple Steps to Bulletproof Your Code
1. Always Use Parameterized Queries
This is non-negotiable. Every modern framework supports parameterized queries:
// DO THIS - Safe from SQL injection
app.get('/user/:id', (req, res) => {
    const query = 'SELECT * FROM users WHERE id = ?';
    db.query(query, [req.params.id], (err, result) => {
        res.json(result);
    });
});
2. Implement Input Validation
Never trust user input. Ever. Validate everything:
const validateUserId = (id) => {
    const numericId = parseInt(id);
    if (isNaN(numericId) || numericId < 1) {
        throw new Error('Invalid user ID');
    }
    return numericId;
};
3. Apply the Principle of Least Privilege
Your application database user shouldn’t have admin privileges:
-- Create a limited user for your application
CREATE USER 'app_user'@'localhost' IDENTIFIED BY 'strong_password';
GRANT SELECT, INSERT, UPDATE ON myapp.* TO 'app_user'@'localhost';
-- Never grant unnecessary permissions like DROP, CREATE, ALTER
The New Attack Vectors You’re Not Thinking About
A new type of SQL injection has emerged in 2019, “Voice-Command SQL Injection”. As the name suggests, this attack relies on voice commands. As we integrate more voice assistants and IoT devices into our applications, the attack surface expands.
Additionally, Over 20% of closed source projects scanned are vulnerable to SQL injection when they first start using security tooling. This means one in five applications goes into production with SQL injection vulnerabilities.
Your Action Plan Starting Today
Audit Your Existing Code: Search for string concatenation in SQL queries. Every instance is a potential vulnerability.
Implement Automated Testing: Tools like SQLMap can identify vulnerabilities before attackers do.
Education is Key: 88 percent of cybersecurity breaches are caused by human error. Regular security training isn’t optional it’s essential.
Monitor and Log: The average time to identify a breach is 194 days. Proper logging can reduce this dramatically.
The Bottom Line
SQL injection isn’t a theoretical risk it’s an active threat costing businesses billions annually. The technology to prevent it exists, has been refined over decades, and is built into every modern development framework.
The question isn’t whether you can prevent SQL injection. It’s whether you will.
As developers, we’re the first and often last line of defense against these attacks. Every parameterized query you write, every input you validate, and every security best practice you follow is a barrier between attackers and the data we’re trusted to protect.
The next time you’re tempted to concatenate user input into a SQL query because it’s just a small internal tool or we’ll fix it later, remember the companies that thought the same thing right up until they made headlines for all the wrong reasons.
Ready to secure your applications? Check out my comprehensive guide: SQL Injection Attacks: What Developers Need to Know for code examples, framework-specific solutions, and detailed prevention strategies.
메타데이터
- post_id
- ca614b7296b1
- slug
- sql-injection-attacks-cost-companies-8-7m-heres-what-every-developer-must-know-ca614b7296b1
- url
- https://medium.com/@zahirbdby/sql-injection-attacks-cost-companies-8-7m-heres-what-every-developer-must-know-ca614b7296b1
- canonical_url
- https://medium.com/@zahirbdby/sql-injection-attacks-cost-companies-8-7m-heres-what-every-developer-must-know-ca614b7296b1
- author_url
- https://medium.com/@zahirbdby
- status
- ok
- fetched_at
- 2026-06-20 20:29:01