From IPaaS to MCP Server: How to Turn Your Enterprise API Estate into a Semantic Layer That AI…
Enterprise API
From IPaaS to MCP Server: How to Turn Your Enterprise API Estate into a Semantic Layer That AI Agents Can Actually Use
Enterprise API
Disclosure: I use GPT search to collection facts. The entire article is drafted by me.
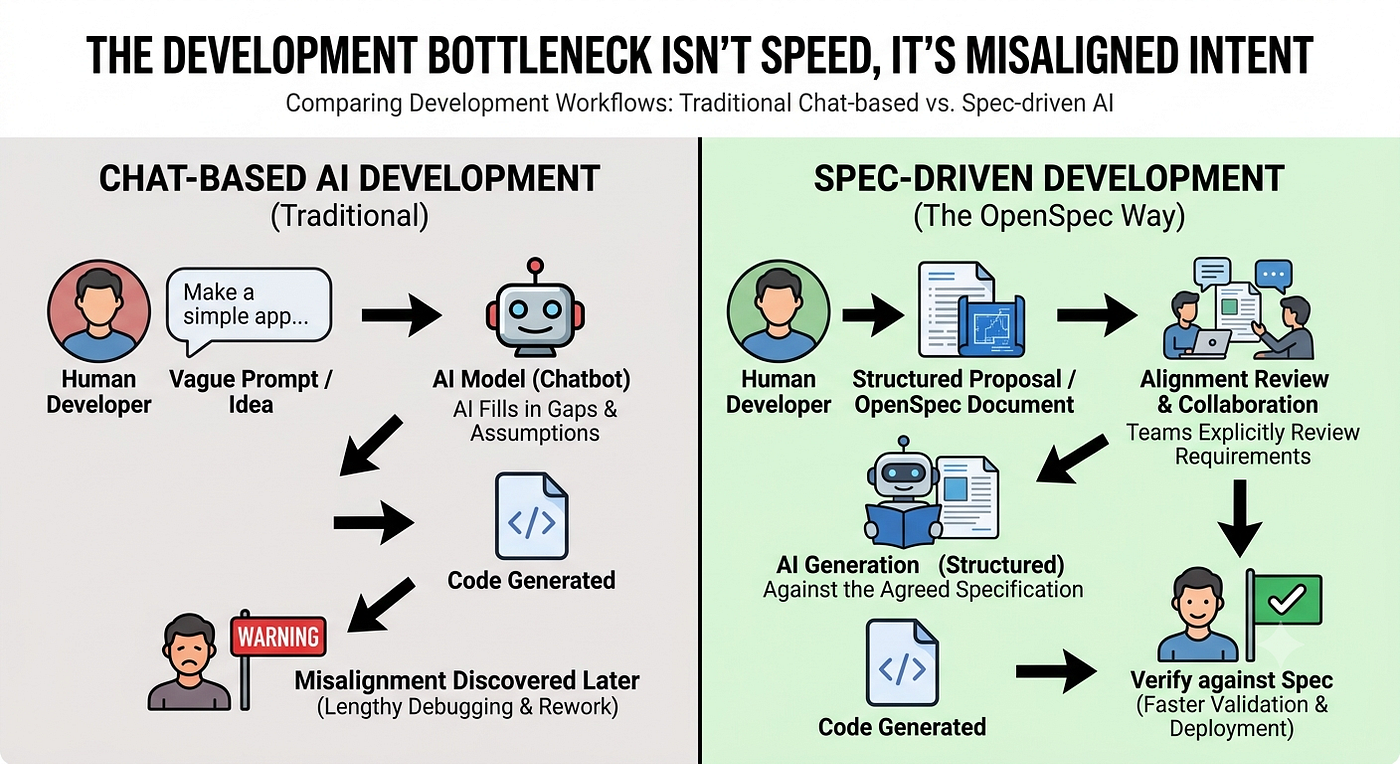
Most enterprises don’t have an integration problem anymore. They have an interpretation problem.
The APIs exist. The pipelines are running. The ESB has been humming for years. The iPaaS platform handles authentication, routing, transformation, and retry logic — all of it. You’ve spent real money building this infrastructure, and it works.
The problem is that none of it was designed to be understood by a model.
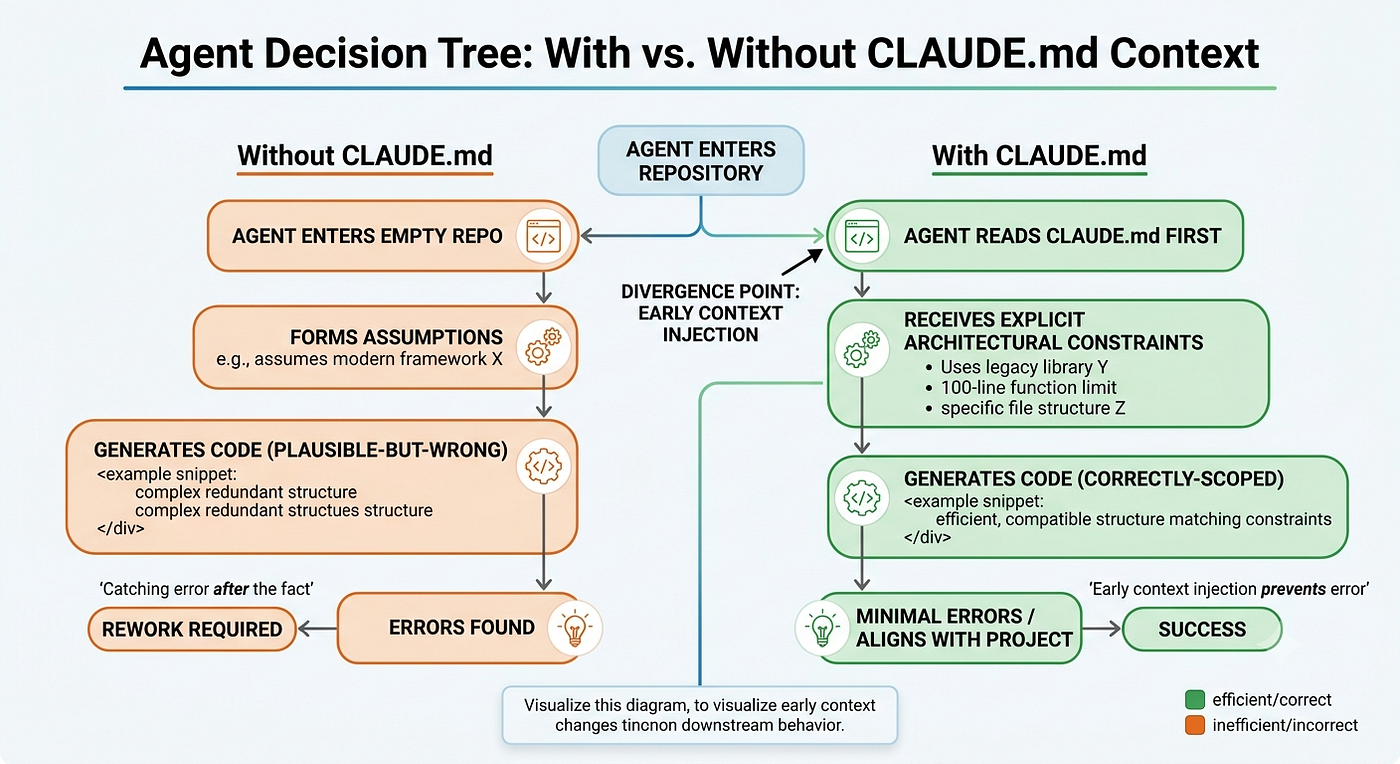
When an AI agent hits your API gateway, it doesn’t see “business capabilities.” It sees a list of endpoints with names like POST /v2/contract/query/advanced and parameters like filterType: INT and pageToken: STRING. It sees a schema that was designed for a developer who had two hours of onboarding, a Confluence page, and a Slack channel to ask questions. Not for a language model that has to infer intent from a JSON blob.
This is the actual problem that MCP — the Model Context Protocol — is trying to solve. And if you already have an iPaaS platform managing your enterprise API estate, you’re closer to the solution than you think. But only if you understand what the translation actually requires.
What MCP Actually Is (And What It Isn’t)
MCP was introduced by Anthropic in November 2024 as an open standard for connecting AI systems with external tools, data sources, and services. By early 2026, the ecosystem had grown to over 10,000 active servers and 97 million monthly SDK downloads. OpenAI adopted it in March 2025. Google DeepMind followed. The protocol re-uses the message-flow ideas of the Language Server Protocol and runs over JSON-RPC 2.0.
That background matters only so you understand that MCP is not a startup’s proprietary vendor lock-in play. It’s a quickly-hardening open standard.
But here’s what MCP is not: it’s not a replacement for your API gateway. It’s not a new integration platform. It’s not a chatbot wrapper. And it’s definitely not something you can install and call it done.
MCP defines three core capability types:
- Tools: Executable actions the AI can invoke — think API calls, database queries, computation. These have side effects. The model calls them when it needs to do something.
- Resources: Read-only data the AI can access for context. No side effects, just structured retrieval. Think reference data, lookup tables, and configuration context.
- Prompts: Predefined prompt templates and workflow instructions that servers can supply. These tell the model how to use the other capabilities.
The mental model is clean: Tools give the model hands, Resources give it eyes, Prompts give it training wheels.
What the protocol does not define — and what you have to bring yourself — is the semantic quality of what you put into each of these categories. That’s entirely on you.
Why the iPaaS Connection Is More Than Convenient
Here’s the architectural insight that most people miss:
iPaaS was built to solve system interoperability. How does Salesforce talk to SAP? How does a webhook from Stripe trigger an update in your ERP? It handles protocol translation, authentication orchestration, data transformation, retry logic, and routing.
MCP is built to solve model-system interoperability. How does a language model understand what your system can do? How does it know which tool to call, with what parameters, under what constraints?
These are two different problems operating at two different abstraction layers. And they’re additive, not competitive.
If you’ve already put your enterprise APIs behind an iPaaS platform, you’ve done something extremely valuable: you’ve centralized governance. Your APIs have authentication policies, rate limits, logging, and transformation already applied. When you now expose those through MCP, you’re not starting from scratch. You’re adding a semantic layer on top of an already-governed layer.
This is exactly why IBM has publicly positioned iPaaS as foundational to AI strategy — iPaaS principles form the backbone of a scalable agent integration approach. The embedded iPaaS platforms that are evolving right now are explicitly adding MCP server support, LLM tool calls, and RAG data syncs as first-class features.
The enterprise that gets this right doesn’t rebuild its integration layer for AI. They surface it.

AI Generated Image
The Three-Layer Reconstruction (Not a Migration)
Let’s be precise about what “exposing your iPaaS as an MCP Server” actually means in practice.
Layer One: Translating OpenAPI Into Business Tools
Most enterprise APIs already have OpenAPI documentation. OpenAPI is language-agnostic, human-readable, and machine-parseable. It defines the structural contract of an API: paths, parameters, response schemas, and authentication mechanisms.
What OpenAPI does not define is business intent. It tells you what the API accepts. It doesn’t tell a model why you’d ever call it, or what real business question it answers.
The first translation step is mapping your well-documented OpenAPI interfaces into semantically named MCP tools. The naming principle is simple: describe the business action, not the technical operation.
Not POST /v2/contract/query/advanced — but query_contracts_by_amount_and_period.
Not GET /supplier/risk/check — but search_supplier_risk_profile.
Not GET /order/status/{id} — but get_sales_order_status.
This sounds trivial. It isn’t. The names and descriptions you assign to your MCP tools become the primary signal the model uses to decide whether and when to invoke them. A well-named tool with a clear description is worth ten poorly described ones. Here’s a minimal but effective pattern in Python using the FastMCP approach:
from fastmcp import FastMCP

mcp = FastMCP("enterprise-capabilities")
@mcp.tool(
    description="""
    Query contracts by signing period and minimum value.
    Returns contract header data and counterparty aggregations.
    Does NOT include sensitive attachments or personal data fields.
    Use this when the user asks about contract volume, counterparty exposure,
    or contractual commitments within a date range.
    """
)
def query_contracts_by_amount_and_period(
    start_date: str,
    end_date: str,
    min_value: float,
    currency: str = "USD"
) -> dict:
    # Delegates to iPaaS endpoint - all auth, logging, and rate limiting
    # handled at the gateway layer, not here
    return ipaas_client.call(
        endpoint="/v2/contract/query/advanced",
        params={
            "dateFrom": start_date,
            "dateTo": end_date,
            "filterType": 1,
            "minAmount": min_value,
            "currency": currency
        }
    )
Notice what this code does: the tool description is longer than the function body. That’s intentional. The description is not documentation for engineers. It’s the runtime context for the model. It tells the model when to use this tool, what it returns, and — critically — what it does not return. That last part is how you prevent the model from making wrong assumptions about data completeness.
The iPaaS client underneath handles everything else: OAuth token refresh, retry on 5xx, response transformation, audit logging. Your MCP Server doesn’t need to re-implement any of that.
Layer Two: Making Tools Discoverable Through Metadata
A single MCP server in an enterprise context might expose 40, 80, or 150 tools. At that scale, the model can’t reliably scan all tool descriptions during every inference pass — the context window becomes a bottleneck, and selection accuracy degrades.
The solution is organizational. You group tools into business domain namespaces. You tag resources by access level. You create prompt templates that guide the model toward the right tool cluster for common workflow patterns.
In practice, this looks like:
- A
financenamespace for tools covering AP, AR, contracts, invoicing, settlement - A
supply_chainnamespace for procurement, supplier risk, inventory, logistics - A
hrnamespace for headcount, onboarding status, org structure queries - An
opsnamespace for order status, SLA tracking, escalation triggers
Each namespace becomes a business directory. The model, when given a query about “Q3 invoice settlement by vendor,” doesn’t need to scan 150 tools. It navigates to finance, finds the relevant tool cluster, and operates within a scoped context.
The MCP Resources capability is the right place to put this directory. Resources are read-only and contextual — they’re exactly right for making the tool catalog navigable without exposing execution surfaces. The pattern from the MCP community is instructive: treat resources as the “readme file” — a one-shot guide for the model on how to navigate your capability space.
Layer Three: Keeping Governance at the Platform, Not the Model
Here’s the mistake I see most often when teams rush to build MCP integrations: they delegate governance decisions to the model.
“The model will only call what it needs to.” “The descriptions are clear enough that they won’t misuse the tool.” “We’ll add guardrails later.”
This is exactly backwards. The model should never be the last line of defense.
MCP’s official specification on HTTP transport explicitly includes an authorization flow — the protocol is designed so clients can act on behalf of resource owners within defined permission scopes. This isn’t an optional ceremony. It’s the architectural contract the protocol is built around.
Your iPaaS platform already has everything you need here: OAuth 2.0 flows, role-based access control, rate limiting, field-level masking, audit trails. The MCP Server’s job is to delegate authorization back to the platform, not to re-implement it.
The MCP 2026 roadmap explicitly calls out the gaps that production teams are hitting: end-to-end audit trails that feed into compliance pipelines, enterprise-managed auth that moves away from static secrets toward SSO-integrated flows, and configuration portability across clients. These are on the official roadmap because production enterprise deployments have shown that without them, the protocol works in demos but struggles in regulated environments.
The practical rule: every tool should fail safely with a clear authorization error before it ever produces a data result for an unauthorized caller. Governance doesn’t get retrofitted. It gets designed in from the first tool definition.

AI Generated Image
The Contract Analysis Use Case (Where This Becomes Real)
Abstract architecture is only as convincing as the concrete scenario it produces.
Consider this real enterprise workflow: A CFO wants to know which counterparties have outstanding contracts above $500K expiring in Q4 2026, segmented by business unit, with a flag for any counterparties that also have open receivables. Historically, this took three teams — legal, finance, and data — about a week. The output was an Excel file with known data quality issues.
With a properly constructed MCP layer over an existing iPaaS platform, the workflow becomes:
- The CFO (or their analyst) types the query in natural language into an AI agent interface
- The model identifies three tool invocations:
query_contracts_by_expiry_and_value,get_receivables_status_by_counterparty,aggregate_by_business_unit - Each tool call routes through the MCP Server, which delegates to the iPaaS layer
- The iPaaS layer applies authentication (OAuth token for the CFO’s identity), validates permissions (they can see contract headers but not legal annexes), applies rate limiting, and logs the query
- Structured results return to the model, which generates a formatted summary, a ranked table, and a flag list
The model didn’t write SQL. It didn’t touch the database. It didn’t bypass any governance layer. It used tools that were designed to express business capability, backed by a platform that was designed to enforce business rules.
That’s the actual value proposition. Not “AI can now access your data.” But “AI can now use your governed capabilities, within your defined constraints, in the way you designed.”
The difference is the difference between giving someone a key to your server room and giving them a terminal with defined permissions.
What Most Teams Get Wrong
There are two failure modes I see consistently.
Failure mode one: shipping before describing. Teams expose 60 APIs to MCP in a weekend. None of the tool descriptions is more than one sentence. The parameter names are the original backend identifiers. Return schemas are undocumented. The model gets confused, calls the wrong tools, hallucinates missing fields, and the whole project gets labeled “not ready.”
The protocol didn’t fail. The semantic layer failed. An MCP Server with poor descriptions is worse than no MCP Server — it’s a hall of mirrors that looks like capability but produces confusion.
Failure mode two: bypassing the governance layer. Teams build MCP tools that directly call databases or internal microservices, bypassing the iPaaS/API gateway entirely “for performance.” This produces a fast demo and a governance nightmare. When the audit comes, there’s no record of what the model queried. When a rogue agent calls a destructive endpoint, there’s no kill switch. When a field needs masking for GDPR, there’s nowhere to insert the masking logic.
The MCP threat taxonomy published in early 2026 catalogs 38 distinct threat categories for MCP systems, including tool description poisoning, indirect prompt injection, and dynamic trust violations — none of which are adequately covered by traditional security frameworks. These aren’t theoretical. They’re production failure modes from real enterprise deployments.
The governance layer is not a performance tax. It’s the entire point.
My Actual Judgment on Where This Is Going
MCP is not hype. It’s also not finished.
The production readiness research published in early 2026 is explicit: three critical protocol-level primitives are still missing from the specification — identity propagation across multi-agent chains, adaptive tool budgeting for complex workflows, and structured error semantics for deterministic agent recovery. These gaps don’t make MCP unusable. But they mean that enterprise-grade deployments right now require you to engineer compensating controls at the application layer.
The teams that are ahead of this curve are not the ones who moved fastest. They’re the ones who treated the MCP layer as a product — with intentional naming, versioning, description governance, and a registry of what’s been published and to whom.
The MCP Registry preview, launched in 2025, pointed at exactly where the ecosystem is heading: centralized discoverability and distribution of MCP server capabilities. This means the semantic assets you build today — the tool definitions, the descriptions, the governance policies — become reusable, shareable, and composable across your AI platform ecosystem. A well-built MCP layer for your contracts domain becomes a building block for every agent that ever needs to touch contracts. You build it once; every future workflow inherits it.
This is the asset value that iPaaS teams haven’t fully articulated to their organizations yet. The integration work they’ve done is not just infrastructure maintenance. It’s an inventory of governed business capabilities. MCP is the interface that makes that inventory accessible to the model layer.
The Conclusion You Can Actually Act On
Here is what this all collapses to:
Before you touch MCP tooling: audit your API estate for semantic quality. Can a non-engineer read your endpoint list and understand what business problem each one solves? If not, fix that first.
When you build your MCP Server: spend more time on descriptions than on code. The code is a thin wrapper. The descriptions are the product.
Keep iPaaS in the stack, not around it. Your governance, authentication, auditing, and transformation logic should stay at the platform layer. The MCP Server delegates to it; it doesn’t replace it.
Start with one domain, do it completely. A finance domain with 12 well-described, properly governed tools is more valuable than 80 half-documented tools across everything. Quality compounds.
Design for the audit trail from day one. Every tool invocation should produce a log entry that satisfies the same compliance requirements as a direct API call. Because legally, it is one.
The model doesn’t make your business capabilities smart. It makes the semantic interface to your business capabilities legible. Your job is to build the best possible semantic interface.
Everything else is just plumbing.
If you’d like to show your appreciation, you can support me through:
✨ **Patreon ✨ [Ko-fi](https://ko-fi.com/jinlowmedium) ✨ [BuyMeACoffee](https://buymeacoffee.com/jinlowmedium)**
Every contribution, big or small, fuels my creativity and means the world to me. Thank you for being a part of this journey!
메타데이터
- post_id
- d27aebb2d23e
- slug
- from-ipaas-to-mcp-server-how-to-turn-your-enterprise-api-estate-into-a-semantic-layer-that-ai-d27aebb2d23e
- url
- https://medium.com/jin-system-architect/from-ipaas-to-mcp-server-how-to-turn-your-enterprise-api-estate-into-a-semantic-layer-that-ai-d27aebb2d23e
- canonical_url
- https://medium.com/jin-system-architect/from-ipaas-to-mcp-server-how-to-turn-your-enterprise-api-estate-into-a-semantic-layer-that-ai-d27aebb2d23e
- author_url
- https://medium.com/@jinlow
- status
- ok
- fetched_at
- 2026-06-13 07:35:29