PicoCTF2024: Trickster
In this write-up , i will show you how did i solve Trickster challenge from picoCTF 2024.
PicoCTF2024: Trickster
In this write-up , i will show you how did i solve Trickster challenge from picoCTF 2024.
Tags: Web Exploration, picoCTF2024, browser_webshell_solvable

let’s launch the instance…

After launching the instance we got the above image upload website. next, we look for hidden directories on this site using robots.txt and explore some of them.

so, here there are two folders what is in the /instructions.txt
Let's create a web app for PNG Images processing.
It needs to:
Allow users to upload PNG images
    look for ".png" extension in the submitted files
    make sure the magic bytes match (not sure what this is exactly but wikipedia says that the first few bytes contain 'PNG' in hexadecimal: "50 4E 47" )
after validation, store the uploaded files so that the admin can retrieve them later and do the necessary processing.
As we understand from the above instruction the photo upload site looks for the “.png” extension in the submitted file and one thing we have to make sure is the first byte contains ‘PNG’ in hexadecimal: “50 4E 47” after this we can embed our php reverse shell script to bypass it. use your favorite hex editor like gedit and create a php reverseshell and make sure to save it .png.php

upload this to the photo upload site …

Now we have successfully uploaded our php script. To access our reverse shell let’s go to /uploads/photo.png.php?cmd=ls

It will list the available directories, in this case our target is the flag so we can use a command like **/uploads/photo.png.php?cmd=cat ../***
The above command will print everything found in the previous directory see in the picture below..
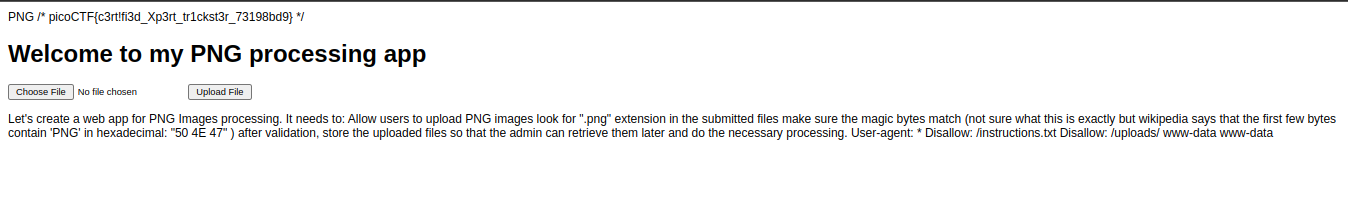
End of story :)
메타데이터
- post_id
- 0a258ad405c2
- slug
- picoctf2024-trickster-0a258ad405c2
- url
- https://medium.com/@yohannestirfe4/picoctf2024-trickster-0a258ad405c2
- canonical_url
- https://medium.com/@yohannestirfe4/picoctf2024-trickster-0a258ad405c2
- author_url
- https://medium.com/@yohannestirfe4
- status
- ok
- fetched_at
- 2026-07-26 16:45:50

