Blockchain under the Hood: P2P Networks, Cryptography, Consensus, and Proof of Work — Part 3 of 4
One of the most fascinating aspects of blockchain is how it brings together ideas from multiple disciplines — computer science, distributed…
Blockchain under the Hood: P2P Networks, Cryptography, Consensus, and Proof of Work — Part 3 of 4
One of the most fascinating aspects of blockchain is how it brings together ideas from multiple disciplines — computer science, distributed systems, cryptography, economics, and even game theory — and assembles them into a single, powerful framework.
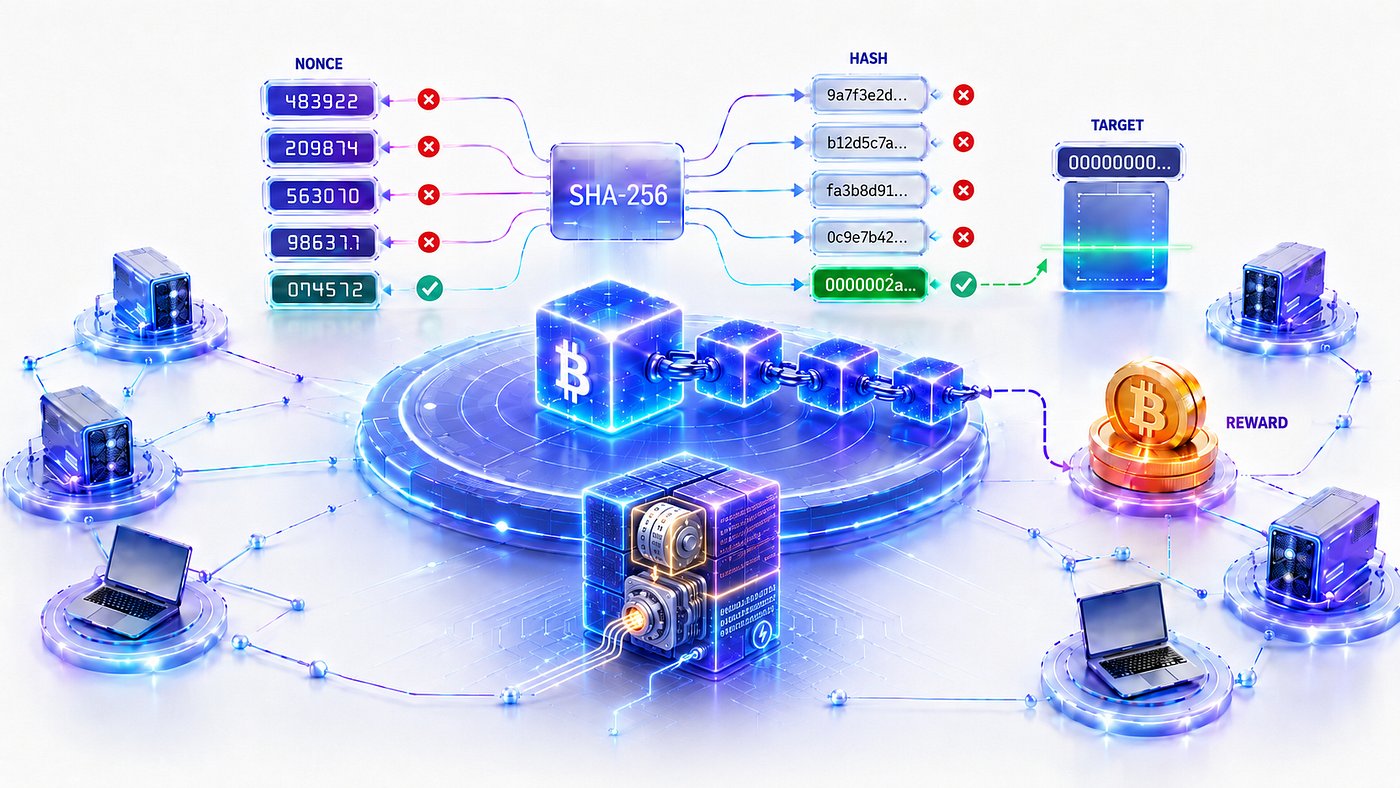
This is Part 3 of a four-part series, where we’ll talk about mining — one of the most elegant pieces of engineering in the entire blockchain puzzle.
- Part 1: What is Blockchain? + Hash Cryptography Read here
- Part 2: Immutable Ledger + Distributed P2P Network Read here
- Part 3: How Mining Works (you’re here)
- Part 4: Consensus Protocols Read here
In Part 2, we saw why blockchain is more than just a chain of linked blocks. Cryptographic hashes make tampering visible, and a distributed P2P network makes unilateral rewriting much harder. Between those two layers of security, blockchain becomes something genuinely difficult to attack.
But one major question still remains: if there is no central authority, who gets to add the next block?
That is exactly the problem mining solves. And in this part, we finally look at the piece of blockchain that most people have heard about, but very few people actually unpack properly.
At a high level, mining is often described as “creating new coins.” That’s not wrong — but it’s not the deepest way to understand it. Mining is really about something more fundamental: it is the mechanism by which a decentralised network agrees on what the next valid block looks like, without needing anyone to be in charge. The coin reward is the incentive layer on top of that process, not the process itself.
So let’s unpack it properly — starting from the inside of a block.
What’s Inside a Block?
To understand mining, we first need to be very precise about what a block actually contains. A block in a blockchain consists of the following components:
- Block No. — used to identify the position of the block in the blockchain. The first block in the chain is called the Genesis Block (Block #0).
- Data — the main contents of the block. In many blockchains, this is a list of transactions. In other blockchain-style systems, it could represent records, votes, contracts, or any other data the network is designed to preserve.
- Prev. Hash — the hash value of the previous block in the chain. The Genesis Block has this value set to
00000…00since there's nothing before it. - Hash — the unique fingerprint of this block, computed from all its other components.
(And a new concept not covered in Part 1)
- Nonce — short for Number Used Once. This is a number that can be freely changed. It has no meaning in itself — its only job is to give the miner a lever to pull.

The underlying formula is:
hash(block) = f(block number, data, prev. hash, nonce)Here’s the crucial insight: the block number, data, and previous hash of a block are all fixed — a miner cannot change them without invalidating the block or breaking the chain. The nonce is the only variable in the equation. It is the only thing a miner can actually modify.
Everything about mining flows from this single fact.
The Nonce: The Miner’s Main Knob
Having a nonce in a block allows the miner to implicitly control the block’s hash, and that control comes directly from a property we already know about from Part 1 — the avalanche effect.
Because of the avalanche effect, even the smallest change to the nonce — say, incrementing it by 1 — produces a completely different hash. Not a similar one. Not a slightly shifted one. An entirely unrelated 64-character output.

So: turn the nonce dial one click, and you get a brand new hash to evaluate. Turn it again, another completely new hash. There is no pattern, no gradient, no way to inch towards a target. Each attempt is an independent roll of the dice.
This is important to keep in mind as we look at what miners are actually trying to achieve.
The Objective of Mining
Loosely put, the objective of mining is:
Change the nonce of the block in order to manipulate its hash, so that the hash meets a certain criteria.
Now — what exactly is that criterion?
To understand it, we need to take a step back and recognize something that most people never realize about hashes.
A hash is not just a weird-looking string of letters and numbers. It is a number.
Reading a Hash as a Number
SHA-256 produces a 256-bit output, which is typically represented as a 64-character hexadecimal string. In hexadecimal (base-16), each digit can be one of 16 possible values:
0 1 2 3 4 5 6 7 8 9 A(=10) B(=11) C(=12) D(=13) E(=14) F(=15)This means every hash can be directly read as a number in decimal format. For example:
  (93721B87242BE7506017482192202796953DBA99A183CE914B44280AA1A500D1)₁₆
= (9 × 16⁶³) + (3 × 16⁶²) + ... + (13 × 16¹) + (1 × 16⁰)
= (66691599297678361696281547925835809782993887241051343732157498235255469179089)₁₀
That 64-character hex string is just a number — a very, very large one — written in a different base.
So in total, there are 16⁶⁴ possible 64-digit hexadecimal hashes in existence. The smallest possible hash has all 64 digits as zeroes:
0000000000000000000000000000000000000000000000000000000000000000And the largest has all 64 digits as F:
FFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFAll possible hashes live somewhere between these two extremes. And there is one more thing worth noticing: the more leading zeroes a hash has, the smaller its numeric value. A hash starting with twenty-four zeroes is astronomically smaller than one that begins with 5150.... This observation is the key to understanding how mining actually works.
The Universe of All Possible Hashes
Let’s build a visual model. Imagine we represent all possible 64-digit hashes on a plane. The smallest hash sits at the bottom-left corner. The largest sits at the top-right corner.

Every possible hash is a point somewhere on this plane. Now think about where hashes with many leading zeroes would cluster — they’d be near the bottom, because they represent small numbers. Hashes without leading zeroes would sit towards the top.

Hold this picture in your head. We’ll use it to make the concept of mining’s target crystal clear.
The Target: Drawing a Line Across the Universe
Here is where the objective of mining becomes precise:
The network defines a Target — a cutoff line drawn across the hash universe. The miner must find a nonce such that the resulting hash falls below this line.
Any hash above the target line is invalid and will be rejected by the network. Only hashes that fall below the target line are valid and will be accepted.

In practice, the target is expressed simply as a required number of leading zeroes. The reason leading zeroes work so well as a shorthand is that they’re directly telling you the numeric value of the hash: more leading zeroes means a smaller number, which means a hash below the target line.
For example, say the target requires 4 leading zeroes. Then:
1. 0000625064AAA65E667BC65C2F94299687CECE06… ✅ Valid (4 leading zeroes - below target)
2. 0C99625064AAA65E667BC65C2F94299687CECE06… ❌ Invalid (only 1 leading zero - above target)
3. E998B9BB6B6A7D6C320282FF2E3C4CC53BD17CED… ❌ Invalid (no leading zeroes - well above target)
The precise rule is this: the hash must be less than or equal to the target value encoded by the network. Leading zeroes are simply the visible consequence of that threshold check — and a very intuitive way to communicate how strict the requirement is.
How Mining Actually Works
So now we have all the pieces:
- The nonce is the only variable the miner can change
- Every change to the nonce produces a completely unpredictable new hash
- The network has set a target — the hash must have a certain number of leading zeroes to be valid
The mining process is exactly what you’d expect from this setup: the miner cycles through nonce values, one by one, computing the hash each time and checking whether it meets the target. If it does — block mined. If it doesn’t — try the next nonce.
Nonce = 0    →  hash = E4A3B2...   (no leading zeroes) ✗
Nonce = 1    →  hash = 81FCA2...   (no leading zeroes) ✗
Nonce = 2    →  hash = 3D990F...   (no leading zeroes) ✗
...
Nonce = 3206 →  hash = 0032BA527CAD... (2 leading zeroes, not enough) ✗
...
Nonce = 8903 →  hash = 0000ABC1A4EF... (4 leading zeroes — VALID!) ✓

This might take millions — or even billions — of attempts. There’s no trick, no shortcut, no clever path to the answer. It is pure brute force. And crucially, it is designed to be pure brute force.
Why Brute Force Is the Only Option
You might wonder: isn’t there a smarter way? Can’t miners use some mathematical insight to find the right nonce faster?
No — and this is where the two properties of SHA-256 from Part 1 become absolutely central.
The Avalanche Effect
Because of the avalanche effect, there is no gradient to follow. Looking at the hash produced by Nonce = 8902 tells you absolutely nothing about the hash produced by Nonce = 8903. A hash that’s close to the target doesn’t mean the next nonce will be even closer. Each attempt is an independent, unpredictable roll.
There is no smooth search path, no local adjustment that nudges a bad hash towards a good one. Every attempt starts fresh from scratch.
The One-Way Property
Because of the one-way nature of SHA-256, you can never reverse-engineer the answer. You cannot say “I want a hash starting with 0000... — what nonce produces that?" and compute your way to it. SHA-256 is a one-way street:
You can always do this:    nonce   →  SHA-256  →  hash
You can NEVER do this:     hash    →  SHA-256⁻¹ →  nonce
Together, these two properties guarantee that finding a valid nonce is pure luck governed by probability. The miner with more computational power runs more attempts per second and wins more often — but even the most powerful machine on earth cannot predict the right nonce. It can only try faster.
The Economics: Why Would Anyone Do This?
All of this computation costs real money — electricity, hardware, cooling infrastructure. So why do miners bother?
Because when a miner successfully finds a valid hash, the network rewards them. In cryptocurrency-based Proof-of-Work systems, this reward typically comes through a special protocol-defined reward mechanism. It is not a normal user-to-user transfer; it is how the network compensates the miner for contributing computational work.
The block reward has two components:
- The block subsidy — a fixed number of newly created coins
- Transaction fees — the sum of small fees attached to each transaction included in the block by users who want their transactions processed
In Bitcoin, for example, the subsidy started at 50 BTC per block and halves every 210,000 blocks — an event known as the halving. This predictable schedule is what leads to the 21 million coin cap. As the subsidy shrinks over time, transaction fees gradually take over as the primary incentive for miners to keep doing the work.
This is why blockchain is so naturally suited to supporting a cryptocurrency. There is a direct, automatic mechanism to reward the miners who prove they spent real computational effort. No central bank decides who gets coins. The cryptographic puzzle does.
But here’s something important to be precise about: the coin supply limit and the mining difficulty are related, but they are not the same mechanism.
Difficulty and Supply: Two Different Dials
This is a distinction most beginner explanations blur, and it’s worth getting right.
Mining difficulty controls how hard it is to find the next valid block. Many Proof-of-Work networks periodically adjust the target based on how quickly recent blocks have been found. If blocks are being found too quickly, the target is tightened, making valid hashes rarer. If blocks are being found too slowly, the target is loosened, making valid hashes easier to find.
The purpose of difficulty adjustment is to regulate the tempo of block production, even as the total amount of mining power in the network changes.
Supply, on the other hand, is controlled by the protocol’s reward or issuance rules. Some networks reduce rewards over time. Some may have a fixed maximum supply. Others may follow a different monetary design altogether. But those supply rules are separate from the mining difficulty mechanism.
Essentially: Difficulty regulates Tempo. Issuance rules regulate Supply.
The Target Controls the Rarity of Valid Blocks
Now we can bring the target concept back in a more complete way.
By setting the target to require a certain number of leading zeroes, the network controls how rare valid hashes are. Since SHA-256 behaves like a random number generator from the miner’s perspective, each hash attempt lands somewhere in the universe of all possible hashes with equal probability. The target line divides that universe into a valid region and an invalid region.
More leading zeroes required → valid region becomes a smaller fraction of the universe → on average, more attempts needed to land inside it → harder puzzle → blocks take longer to find.

The network uses this mechanism to keep block production at a stable rate. More miners join → blocks are found too fast → target is tightened → valid hashes become rarer → balance restored.
Mining a Block: The Full Picture
Let’s now walk through the full process a miner follows to mine a block.
Step 1: Collect Transactions — The miner gathers unconfirmed transactions, records, or other data from the network and bundles them into a candidate block.
Step 2: Build the Candidate Block — The miner assembles the information that will be hashed: block number, data, previous hash, and a starting nonce.
Step 3: Hash the Candidate Block — The miner computes the block’s hash using the hash function SHA-256.
Step 4: Check the Result — Does the hash have the required number of leading zeroes? Is its numeric value below the target?
- Yes → Block mined. Broadcast to the network immediately.
- No → Increment the nonce by 1 and go back to Step 3.
Step 5: Nonce Exhausted? If the miner runs through the available nonce values without finding a valid hash, the mining software can modify some other protocol-allowed part of the candidate block, such as metadata, timestamp, transaction selection, transaction ordering, or reward-related data. This creates a fresh set of hash possibilities, and the nonce search begins again.

This process continues until someone — somewhere in the world — finds a valid hash and broadcasts it. Then the race resets for the next block.
Expensive to Create, Cheap to Verify
There is a beautiful asymmetry baked into this design that’s worth pausing on.
Finding a valid hash is expensive — it requires potentially billions of attempts, massive hardware, and enormous electricity consumption.
Verifying a valid hash is cheap — any node on the network can take the proposed block, compute the relevant hash, and check in milliseconds whether it meets the target. If it does, and the transactions are valid, the block is accepted.
This asymmetry is one of the most elegant properties of Proof of Work. Because forging a valid block requires doing the work, but verifying it requires almost none, the system can be simultaneously open to all participants and secure against manipulation.
This expensive-to-create proof is also what gives the chain its historical weight. If an attacker tries to modify an already-mined block, they change the data that feeds into the block’s hash, which destroys the original valid hash. From that point, they don’t just have to redo the work for that one block — they have to redo it for every subsequent block, and then out-race the honest chain, which keeps growing while they’re catching up. The further back the block they want to change, the more accumulated work they have to overcome. This is why deeper blocks are considered far more secure than recent ones.
Mining Pools: The Reality of Modern Mining
The elegant theory of mining assumes individual miners competing for blocks. In the early days of mining, that was closer to reality — individuals could run mining software on their own computers and occasionally win a block.
Today, the reality looks very different.
Mature networks can attract so much mining power that an individual miner may have to wait a very long time before finding a valid block on their own. The variance is simply too high — you could spend enormous electricity costs and win nothing for months.
This is why most mining today happens through mining pools. A pool is a group of miners who combine their computational resources and share the reward when any member of the pool finds a valid block.
**Mining Pool:** A cooperative arrangement where many miners contribute their hashing power to a shared effort. When the pool collectively finds a valid block, the reward is distributed among all members proportional to the work they contributed.
Here’s how pools manage the coordination problem: the pool gives each of its members an easier, customised target to search — much simpler than the network target. When a miner meets this easier target, they submit a “share” to the pool. A share proves the miner is actually working and not freeloading. Only rarely does a share also meet the full network target — and when it does, that miner has found a real block, and the reward gets distributed.
Mining pools don’t change the security model of a network. Every pool still follows the same protocol rules, performs the same kind of hashing, and checks candidate blocks against the same network target. What changes is how the reward risk is distributed among participants. For individual miners, it transforms a boom-or-bust lottery into a steady, predictable income.
Why All of This Creates Security
Let’s zoom out and look at what mining achieves for the blockchain as a whole.
In Part 2, we saw that an attacker trying to alter a past block would need to re-mine that block and all the blocks after it. Now we understand what that actually means: they’d have to redo all the proof-of-work, finding valid nonces for every single block they need to re-mine, faster than the honest network keeps adding new blocks at the end.
The honest network never stops. At the network’s intended rhythm, new blocks continue to be found and added to the chain. So the attacker isn’t just racing against a fixed finish line — they’re racing against a target that keeps moving forward. To succeed, they’d need more than half of the total computational power of the entire network — the infamous 51% attack we covered in Part 2.
This is what “proof of work” means in a deeper sense: the chain represents a record of all the computational effort ever invested in it. Every block is a proof that real work was done. An attacker can’t fake this proof without actually doing the work. And the further back in history they want to go, the more accumulated work they’d have to overcome.
Proof of Work, in short: expensive to create. Cheap to verify. Impossible to fake without doing the work.
Putting It All Together
Mining is, at its core, a cryptographic lottery with very specific rules:
- The ticket is a candidate block containing a nonce you can change
- The winning condition is a hash whose numeric value falls below the network’s target
- The prize is usually a protocol-defined reward, often newly minted cryptocurrency plus transaction fees
- The lottery is run by brute force — no shortcuts, no patterns, no reverse engineering
- The difficulty adjusts to keep the lottery producing winners at the network’s intended rhythm, regardless of how many miners are competing
The elegance of this design is that it solves multiple problems simultaneously:
- It creates a fair, decentralised mechanism for adding blocks to the chain — no one is in charge, but the system still produces a steady output
- It provides a clear, automatic way to reward participants who contribute real work
- It makes tampering with history economically ruinous — you’d have to redo more computational work than the entire honest network has ever done, while it keeps running ahead of you
- It ties the security of the chain to physical reality — electricity, time, and hardware — rather than to any social or institutional trust
Wrapping Up Part 3
In this part, we’ve gone from the anatomy of a block all the way through to the full mechanics of mining. We saw that the nonce is the miner’s only lever, that hashes are really just numbers, that the target draws a line across the universe of all possible hashes, and that finding a valid hash below that line requires pure brute-force effort — enforced by the avalanche effect and the one-way nature of SHA-256.
We also saw that finding a block is expensive, but verifying one is nearly free — and that asymmetry is what gives Proof of Work its power. And we unpacked two concepts that often get muddled: difficulty, which regulates tempo, and the protocol’s issuance rules, which regulate how rewards and supply work.
But one question is still hanging in the air.
When multiple miners around the world are all working simultaneously, it’s possible for two valid blocks to be found at nearly the same time. The network suddenly has two competing versions of the next block. How does it decide which one counts? How does a decentralised network with no central authority converge on a single shared truth?
That is the question of consensus — and it’s where everything from the previous three parts finally clicks together into one coherent picture.
In Part 4, we’ll dive into consensus protocols — how Proof of Work consensus actually works in practice, why the longest chain rule makes sense, and how alternative approaches like Proof of Stake tackle the same problem in a fundamentally different way.
Stay tuned with the next installment as we continue peeling back the layers of Blockchain under the Hood!
- Part 1: What is Blockchain? + Hash Cryptography Read here
- Part 2: Immutable Ledger + Distributed P2P Network Read here
- Part 3: How Mining Works (you’re here)
- Part 4: Consensus Protocols Read here
If you found this helpful, you’re welcome to follow along here or connect with me on LinkedIn.
메타데이터
- post_id
- 193d923614bb
- slug
- blockchain-under-the-hood-p2p-networks-cryptography-consensus-and-proof-of-work-part-3-of-4-193d923614bb
- url
- https://medium.com/@harmeet-singh-bagga/blockchain-under-the-hood-p2p-networks-cryptography-consensus-and-proof-of-work-part-3-of-4-193d923614bb
- canonical_url
- https://medium.com/@harmeet-singh-bagga/blockchain-under-the-hood-p2p-networks-cryptography-consensus-and-proof-of-work-part-3-of-4-193d923614bb
- author_url
- https://medium.com/@harmeet-singh-bagga
- status
- ok
- fetched_at
- 2026-07-25 06:43:36




