Understanding Evil Twin Attack on Wi-Fi Networks with Flipper Zero
generate by bing
Understanding Evil Twin Attack on Wi-Fi Networks with Flipper Zero
generate by bing
What is an Evil Twin Attack?
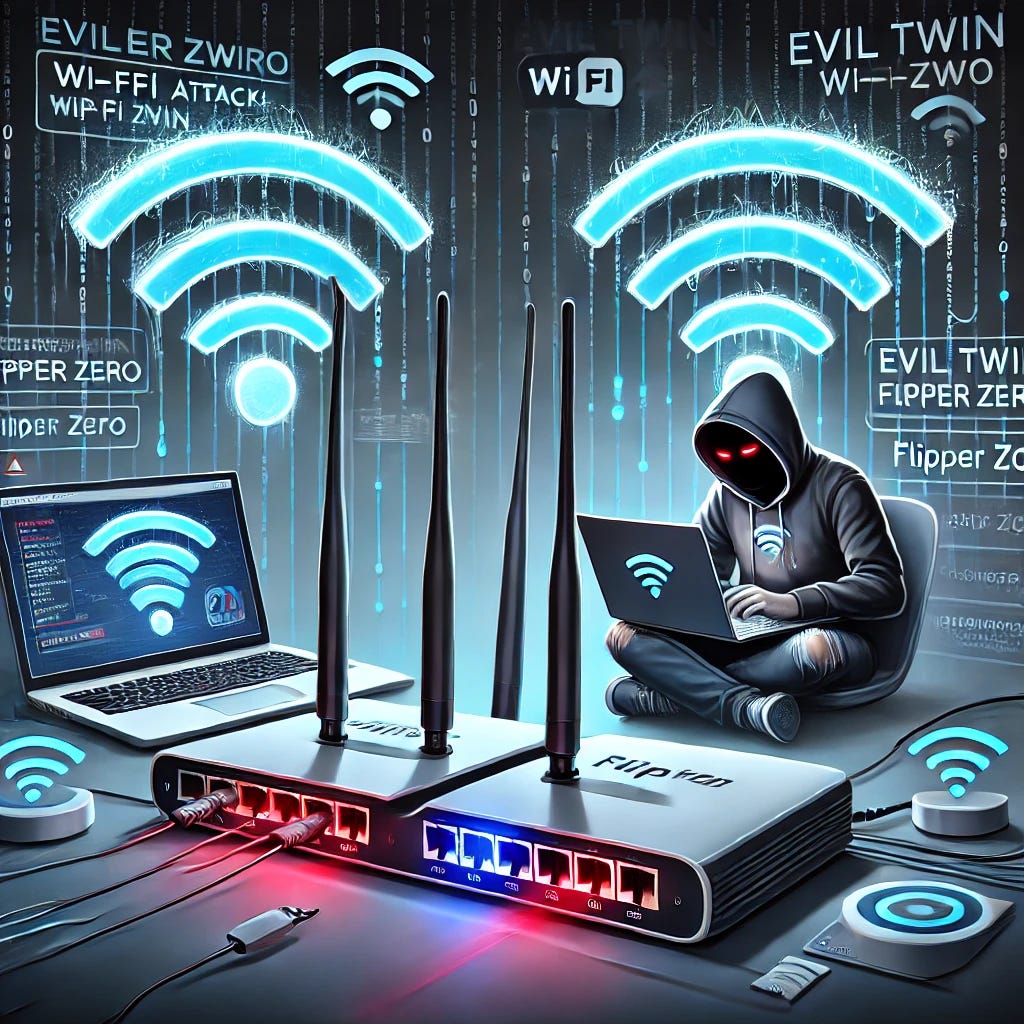
An Evil Twin Attack occurs when a hacker sets up a rogue access point (AP) that looks identical to a legitimate Wi-Fi network. The attacker’s goal is to trick users into connecting to this fake network, where they can intercept communications, capture login credentials, or inject malicious code into the victim’s devices.
How Flipper Zero Can Be Used for Evil Twin Attacks
Flipper Zero is a versatile hacking tool that’s portable and relatively easy to use. Although its design is intended for educational purposes and ethical hacking, in the wrong hands, it can also be used to facilitate Evil Twin Attacks. Here’s how it works:
- Network Scanning and Reconnaissance: Flipper Zero can scan for available Wi-Fi networks in the vicinity. By identifying the target network’s SSID (Service Set Identifier), an attacker can clone it to create an Evil Twin.
- Cloning the SSID and Setting Up the Fake AP: After identifying the legitimate Wi-Fi network’s SSID, the attacker can use Flipper Zero or pair it with tools like the Wi-Fi Pineapple to set up a rogue access point with the same SSID. This fake AP often has a stronger signal, enticing nearby devices to connect to it instead of the genuine one.
- De-authentication Attack: To force legitimate users off the original Wi-Fi network and onto the Evil Twin, attackers can use Flipper Zero to perform a de-authentication (deauth) attack. This attack sends deauth packets to the target, causing their device to disconnect from the legitimate AP. Once disconnected, their device will likely reconnect automatically to the Evil Twin AP, especially if the signal is stronger.
- Capturing Data and Stealing Credentials: Once a user connects to the Evil Twin AP, the attacker can intercept any unencrypted traffic, including login credentials, session cookies, and other sensitive data. By using additional tools (like packet sniffers or dns spoofing), they can capture this information in real-time.

Why Are Evil Twin Attacks Dangerous?
- Stealing Sensitive Information: Attackers can capture usernames, passwords, and even credit card details if the connection is not encrypted (e.g., on HTTP websites).
- Malware Injection: Hackers can redirect users to malicious websites, infecting their devices with malware, ransomware, or other types of malicious code.
- Man-in-the-Middle (MitM) Attacks: Once connected to the fake AP, attackers can manipulate the user’s web traffic, injecting malicious scripts or redirecting them to phishing pages.
How to Protect Against Evil Twin Attacks
- Implement Strong Wi-Fi Security Protocols: Use WPA3 encryption on your wireless networks to ensure that communications are encrypted, making it harder for attackers to intercept data even if they set up an Evil Twin AP.
- Monitor Your Wi-Fi Networks: Use intrusion detection systems (IDS) and Wi-Fi monitoring tools to detect rogue APs. If a new AP with the same SSID as your legitimate network appears, you can take immediate action to investigate and shut it down.
- Educate Users: Train employees to verify the legitimacy of the networks they are connecting to, especially in public places. Encourage them to use VPNs (Virtual Private Networks) whenever connecting to unfamiliar or public Wi-Fi.
- Use Multi-Factor Authentication (MFA): Even if an attacker gains access to a user’s login credentials, MFA can provide an additional layer of protection, preventing unauthorized access to sensitive systems.
- Limit Public Wi-Fi Use: Discourage the use of public Wi-Fi for sensitive tasks such as logging into work email or accessing confidential company systems. If public Wi-Fi must be used, ensure that users are aware of the risks and use encryption tools like VPNs.
Conclusion
The Flipper Zero is an impressive tool that can be used for educational purposes and ethical hacking, but it can also be exploited by malicious actors for Evil Twin Attacks. As a manager, understanding the risks posed by such attacks is crucial for implementing effective security measures in your organization. By strengthening Wi-Fi security, educating employees, and using strong encryption protocols, you can significantly reduce the risk of falling victim to these types of attacks.
Disclaimer: The information provided in this article is solely for educational purposes. It is intended to raise awareness about potential security risks and improve understanding of Wi-Fi network vulnerabilities. The author does not condone or encourage any illegal activities or malicious use of the information presented. The author is not responsible for any criminal actions taken by individuals after reading this article. Always use your knowledge responsibly and ethically.
Source and Reference : https://ittampan.wordpress.com/2024/10/22/understanding-evil-twin-attack-on-wi-fi-networks-with-flipper-zero/
메타데이터
- post_id
- f943c308fdc5
- slug
- understanding-evil-twin-attack-on-wi-fi-networks-with-flipper-zero-f943c308fdc5
- url
- https://osintteam.blog/understanding-evil-twin-attack-on-wi-fi-networks-with-flipper-zero-f943c308fdc5
- canonical_url
- https://osintteam.blog/understanding-evil-twin-attack-on-wi-fi-networks-with-flipper-zero-f943c308fdc5
- author_url
- https://medium.com/@xsanlahci
- status
- ok
- fetched_at
- 2026-07-23 03:25:53